The end-to-end
cybersecurity auditor
Audit experts for every framework, supported by AI-native evidence collection
Trusted by more than 2,000 organizations globally
Reuse evidence across frameworks, automatically matched to overlapping requirements to eliminate duplicate work and accelerate every audit.
SOC 1 and soc 2
From evidence to attestation, simplify your SOC 1 and SOC 2 audit.
HITRUST
Run your HITRUST assessment on one platform.
ISO 27001
Independent ISO 27001 certification with a clear, connected process.
HIPAA
Ensure HIPAA compliance and visibility for your healthcare organization.
PCI DSS
PCI DSS compliance with ASV scans, pentesting, and audits.
GDPR
Protect trust and support growth with automated workflows and integrations.
Steve Kinman
GRC Director
GoTo

Sigita Jurkynaitė
Information Security Manager
Nord Security

Perry Wilson
Director, Information Security
Array Behavioral Care

Gur Brosh
Co-founder & COO
Peach
Thoropass is a licensed auditor that delivers audits, supported by purpose built software to streamline the process. Our platform helps you prepare by organizing evidence and readiness activities, while our audit team performs an independent assessment in accordance with professional standards. This approach allows you to manage preparation and audit execution in one place.
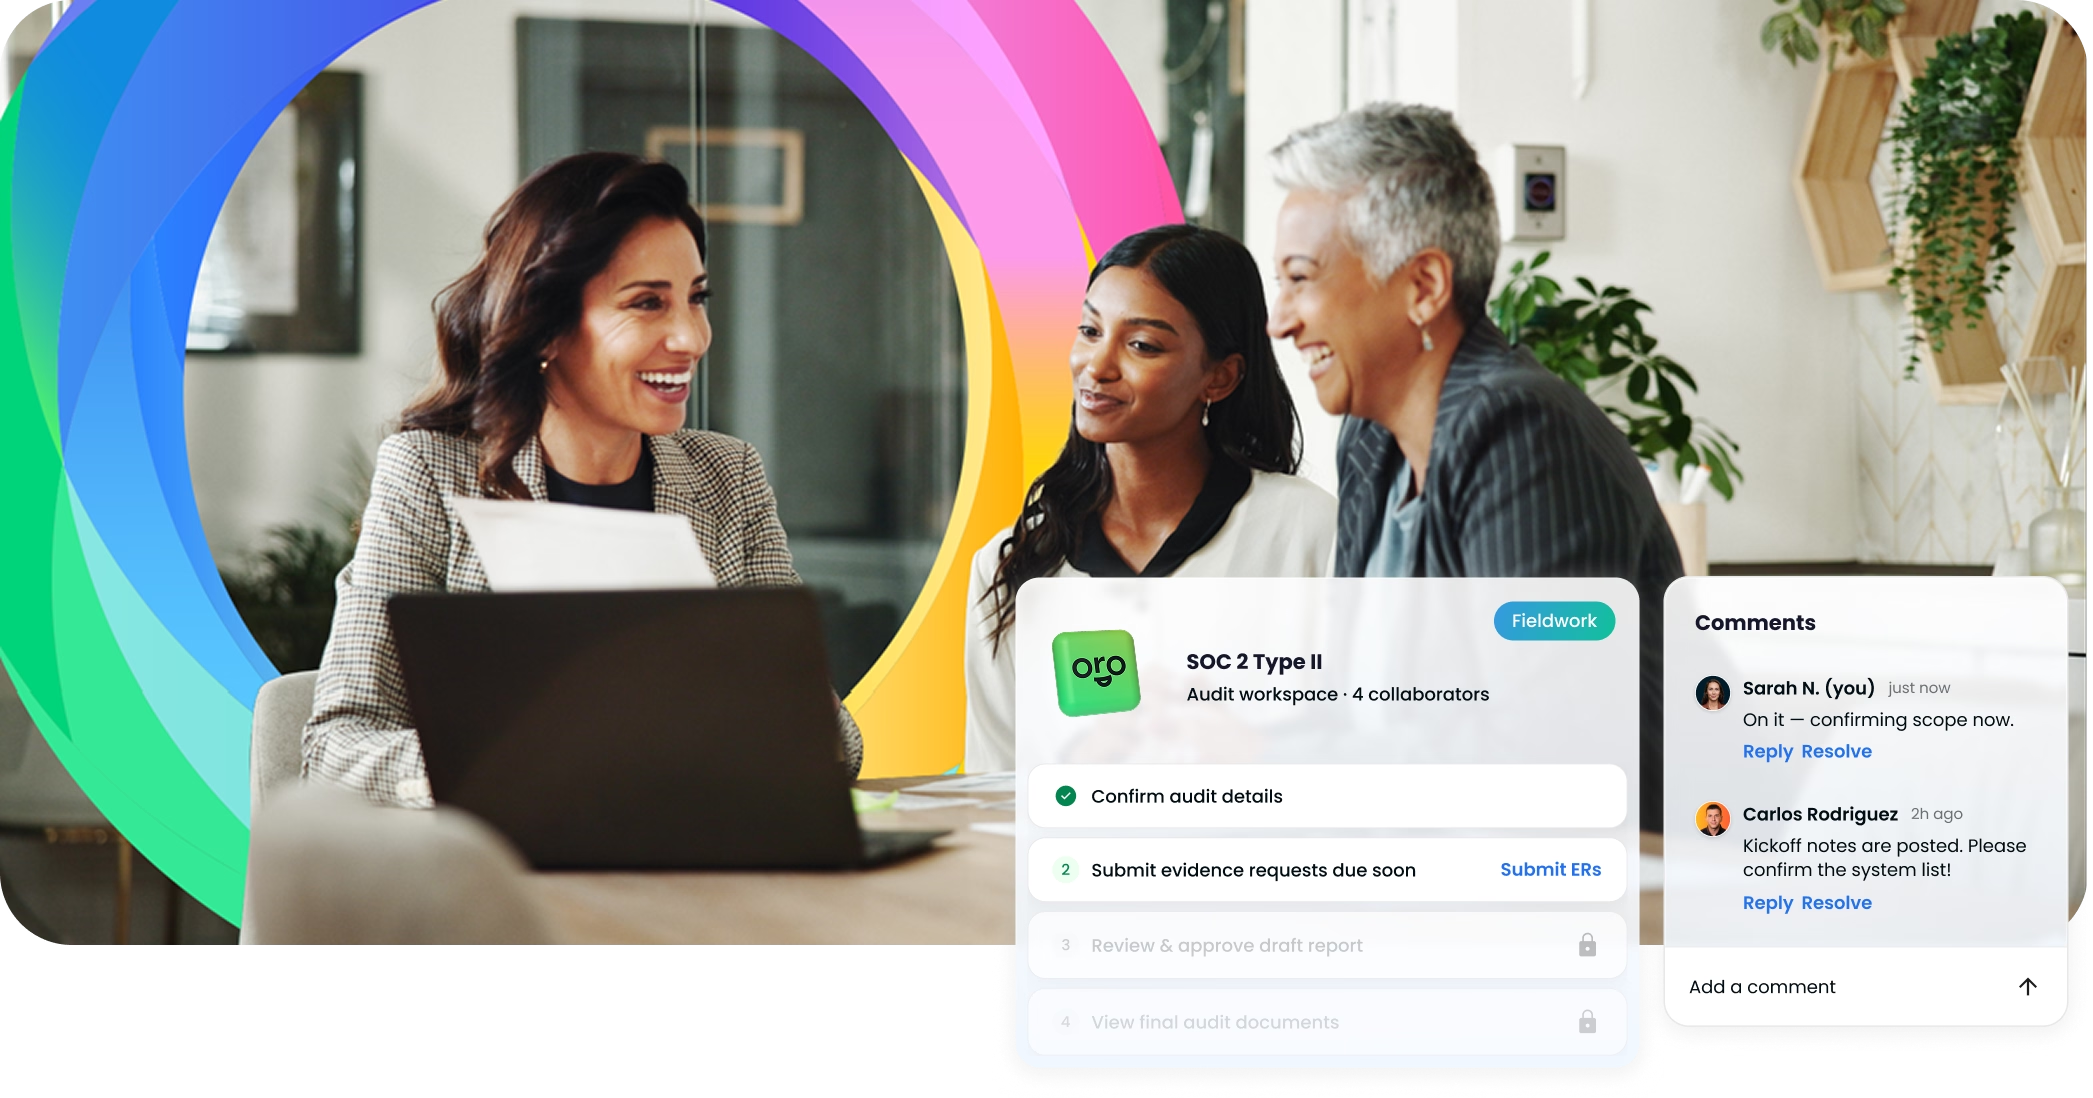
Thoropass reimagines the audit experience by combining a licensed audit firm with an AI-powered platform that automates and streamlines much of the process. Traditional firms often rely on manual evidence collection, spreadsheets, and fragmented communication. In contrast, Thoropass uses AI to map controls, identify gaps, and organize evidence in real time, reducing repetitive work and human error. This results in a more efficient, transparent, and predictable audit process, while still maintaining the rigor and oversight of experienced auditors.
Yes. Thoropass is a licensed audit firm and our audits are conducted according to established professional standards. Thoropass has received the highest AICPA peer review rating for its audit quality. The firm employs experienced auditors and follows rigorous methodologies to ensure accuracy and compliance. In addition, the platform enforces consistency in evidence collection and control validation. This combination of professional oversight and structured workflows helps ensure that audits meet the expectations of regulators, customers, and stakeholders.
Thoropass is designed to support multi-framework audits such as SOC 2, ISO 27001, PCI, GDPR, HITRUST, and others within a unified process. The platform maps overlapping controls across frameworks to reduce duplicate work, allowing organizations to pursue multiple certifications efficiently. It can also accommodate companies with multiple products or environments by organizing evidence and controls in a structured, scalable way, ensuring clarity and consistency across audits.
Organizations can typically get started with Thoropass quickly, often within days. The platform provides guided onboarding, integrations, and a centralized workspace where customers can document and manage their controls, helping accelerate evidence collection. Audit timelines vary depending on scope and readiness, but Thoropass is designed to shorten the overall process compared to traditional approaches. Many customers complete readiness and audit cycles in a matter of weeks to a few months, rather than extended multi-quarter timelines.
The Thoropass Audit Lifecycle Platform is a centralized system that manages the entire audit process from readiness through final reporting. It combines AI-powered workflow automation, evidence collection, control management, and auditor collaboration in one place. The platform is designed to replace fragmented tools like spreadsheets and email chains, providing a structured and transparent approach to compliance that scales with your organization.
“AI-powered” in the context of Thoropass refers to the use of automation and intelligent systems to streamline audit tasks. This includes suggesting relevant controls, identifying gaps, organizing evidence, and reducing manual effort in documentation. AI capabilities help teams prioritize work, improve accuracy, and accelerate readiness. Rather than replacing human judgment, these tools enhance both customer and auditor efficiency throughout the audit lifecycle.
Thoropass integrates with a wide range of common business and infrastructure tools to automate evidence collection and reduce manual work. These typically include cloud providers, identity and access management systems, HR platforms, and ticketing tools. By connecting directly to these systems, Thoropass can continuously gather and validate compliance data, minimizing the need for manual uploads and improving the reliability of audit evidence.
Thoropass pricing varies based on factors such as the frameworks pursued, audit scope, company size, and required services. Because the platform combines software and audit delivery, pricing typically reflects both components. Organizations receive a tailored quote to ensure alignment with their compliance goals. This bundled approach can often be more cost-effective than managing separate vendors for readiness tooling and audit services.
Yes! Thoropass can complement third-party GRC platforms by integrating into your broader compliance ecosystem. While we offer end-to-end audit lifecycle capabilities, organizations can continue using their preferred GRC tools. Thoropass focuses on streamlining audit readiness and execution, and its flexible approach allows teams to avoid duplicating work while maintaining their existing systems.
Thoropass offers a range of penetration testing services designed to identify vulnerabilities across different environments. These typically include network, application, and infrastructure testing, covering both internal and external attack surfaces. The goal is to simulate real-world threats and provide actionable insights to improve security posture. Testing is performed by qualified professionals and aligned with industry standards to support compliance and risk management efforts.
CREST is an internationally recognized accreditation body for cybersecurity professionals and organizations. CREST certification indicates that a penetration testing provider meets rigorous standards for technical capability, methodology, and ethical conduct. Working with CREST-certified testers provides assurance that testing is performed consistently and to a high professional standard, which is often important for regulatory compliance and customer trust.
In many cases, penetration testing is a requirement for cybersecurity frameworks such as SOC 2, HITRUST and others, particularly for demonstrating effective risk management. While requirements vary by framework and scope, a recent and properly conducted pentest is often expected as part of the evidence reviewed during an audit. Even when not strictly required, penetration testing is considered a best practice for identifying and addressing security weaknesses.
Close

Leith Khanafseh
Audit Managing Partner, Thoropass Assurance
Leith founded and leads Thoropass's Assurance practice, bringing 15 years of audit experience to the role. At Thoropass, he oversees the audit and assessment offerings, shapes product direction, and drives innovation that modernizes traditionally outdated audit practices.

Matt Udicious
Director of Infosec Assurance
Matt is a seasoned InfoSec assurance professional with over a decade of experience in cybersecurity, specializing in security, auditing, and compliance.
Matt’s career has included roles, across security, auditing, and compliance. He gained invaluable insights during his tenure as a former auditor, concentrating on SOC 2 compliance for technology companies within the prestigious Big 4 consulting firms. His meticulous approach and deep understanding of industry standards have made him a trusted authority in information security.

Bruce Edwards
Senior Manager, PCI Assurance
Bruce has more than 15 years of experience in security and risk management, both as an external consultant and an internal practitioner. His experience includes penetration testing, PCI QSA, ASV, and cloud security, and in his previous role as a security director, Bruce led PCI DSS assessments for Fortune 500 companies in the fintech and healthcare sectors, both in the U.S. and around the world.

Lucas Baiocchi
Senior Manager, HITRUST InfoSec Assurance
Lucas has more than eight years of experience in information security audits and assessments. As Thoropass’ HITRUST InfoSec Assurance Senior Manager, he leads and executes HITRUST assessments, working closely with organizations to evaluate their security posture, validate control effectiveness, and deliver clear, actionable insights that align compliance objectives with broader business goals. His approach ensures not only regulatory and standards-based compliance, but also the adoption of efficient, scalable, and realistic security solutions.

Tom Miller
Senior Manager, Enterprise Team, InfoSec Solutions
Tom is an information security and technology audit leader with more than a decade of experience delivering assurance engagements for organizations ranging from large public corporations to high-growth startups. He owns Thoropass' largest and most strategic client portfolio, leading complex multi-framework audits and serving as a trusted advisor to executive stakeholders on control design, security requirements, and remediation strategy.

Chris Beiro
Senior Director, InfoSec Solutions
Chris is a seasoned cybersecurity executive with over 15 years’ experience in compliance and audit. He has helped hundreds of organizations – from high-growth startups to Fortune 500 enterprises - strengthen their cybersecurity programs, meet rigorous compliance standards, and mitigate risk. Prior to joining Thoropass, he spent more than 13 years in cybersecurity and audit leadership roles at KPMG and Coalfire.

Austin Newcomer
Senior Manager, InfoSec Assurance
Austin is a Senior Information Assurance leader with more than eight years of experience and expert-level command of AICPA attestation standards. Prior to joining Thoropass, he spent three years at IT auditor Coalfire, where he supported clients ranging from Silicon Valley startups to Fortune 100 corporations.
Today, he leads more than 40 concurrent SOC 1, SOC 2, and HIPAA audits for emerging, mid-market, and enterprise technology companies, with particular depth in healthcare compliance and complex cloud environments across AWS, Azure, and GCP. His work spans the full audit lifecycle — assessing security procedures, reviewing configurations, interviewing control owners, and documenting results — including combined assessments across multiple compliance frameworks.

Emmanuel Amos-Abanyie
Head of Quality Assurance, InfoSec Solutions
As Head of Quality Assurance for InfoSec Solutions, Emmanuel leads the firm's quality assurance program, driving consistency, technical excellence, and standardization across every audit engagement. He works closely with audit teams to strengthen audit methodologies, enhance reporting quality, and promote continuous improvement, helping clients receive accurate, rigorous, and reliable audit deliverables.