Independent certification. Clear process.

Thoropass Certification LLC provides independent ISO 27001 certification audits, helping organizations demonstrate that their Information Security Management System (ISMS) meets internationally recognized standards.

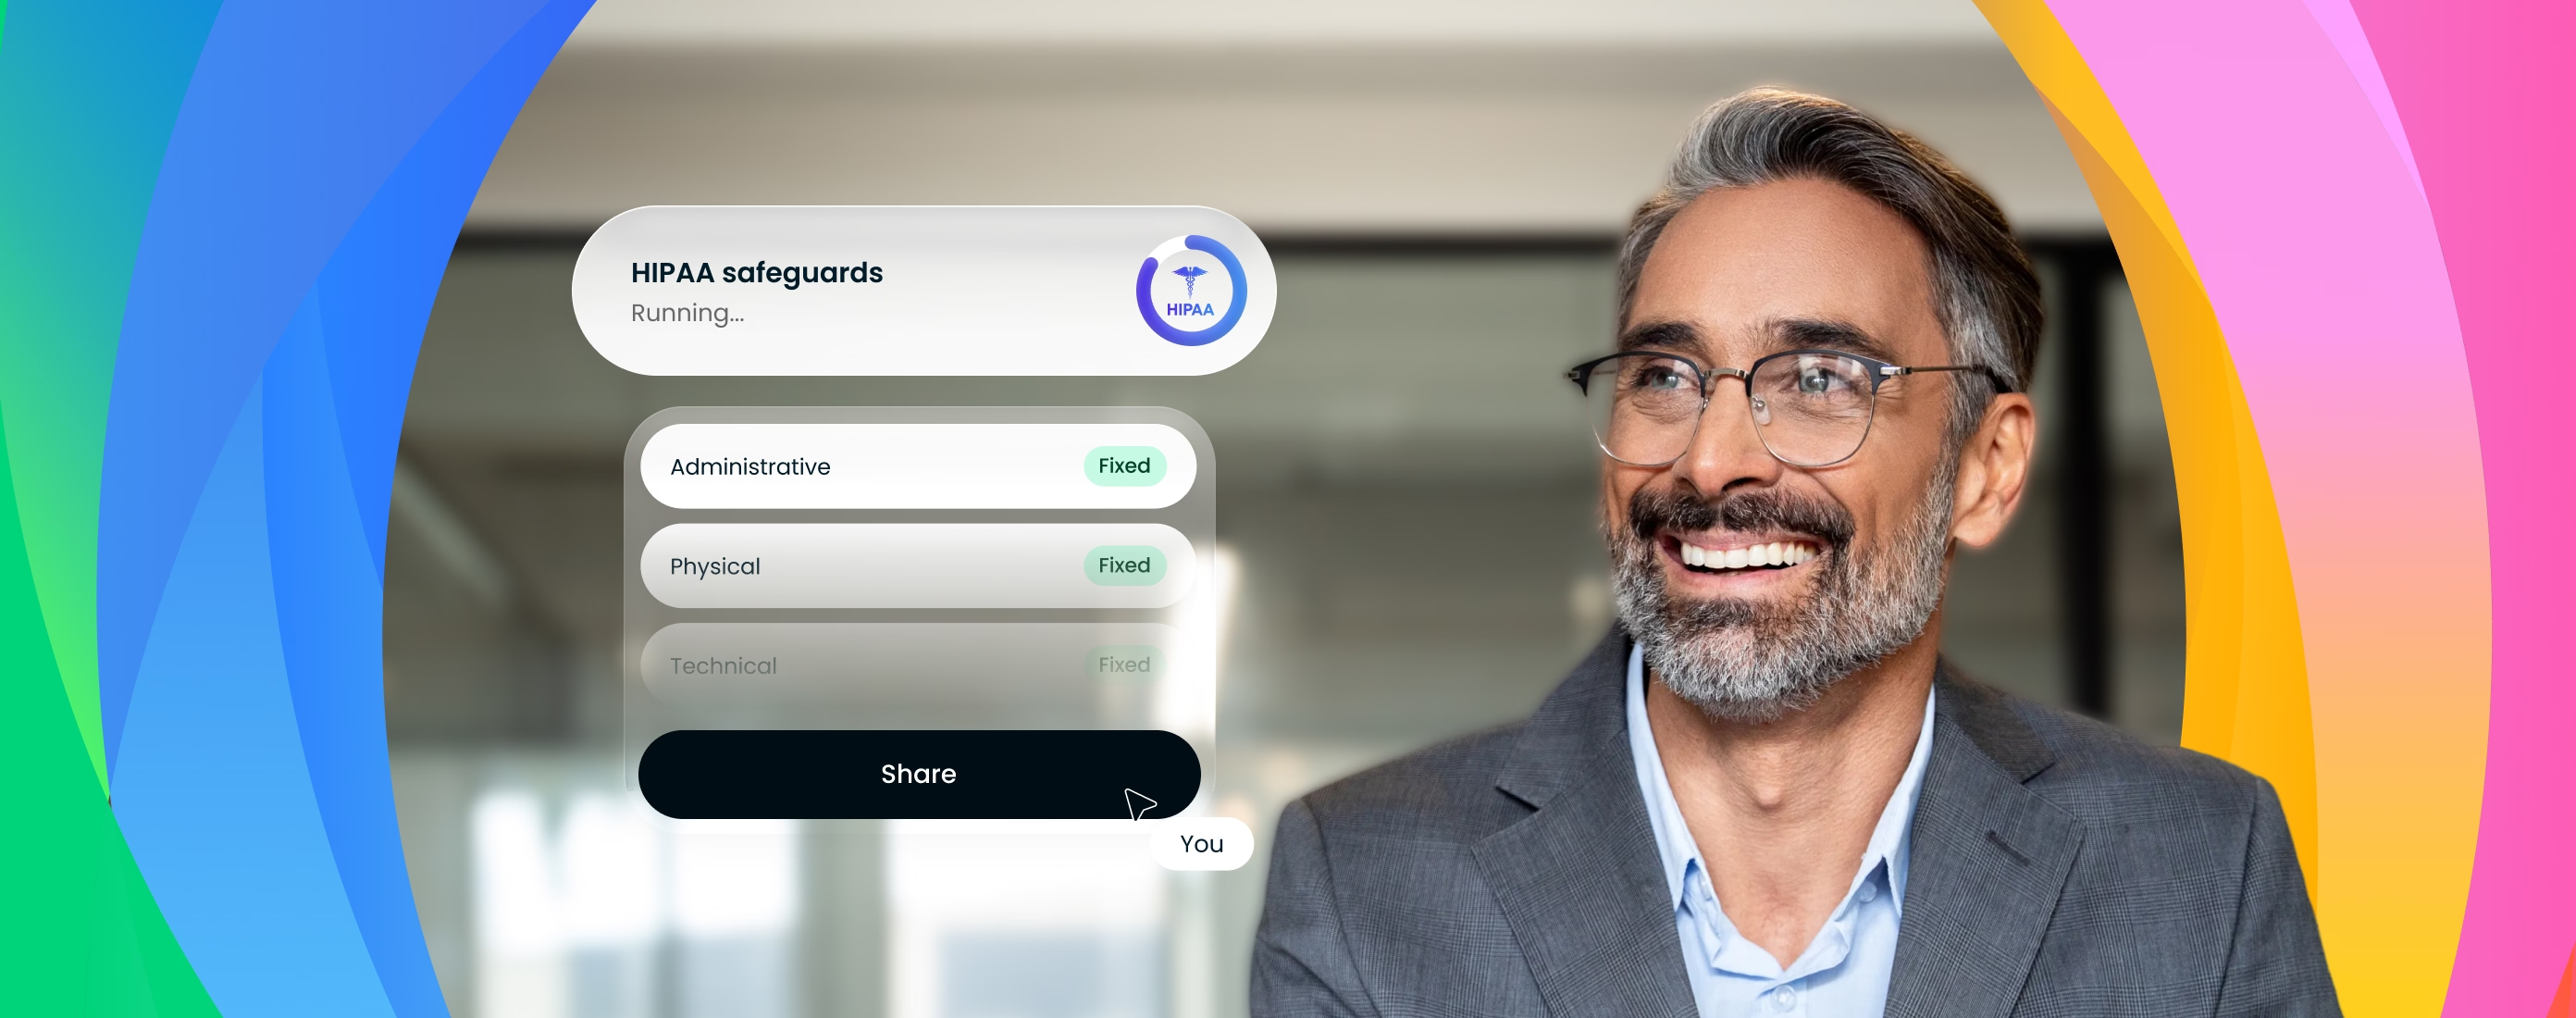
Smiling man with glasses and gray beard wearing a gray blazer and light blue shirt, next to a translucent interface showing HIPAA safeguards status with sections for Administrative and Physical marked 'Fixed' and Technical grayed out, all set against a colorful gradient background.

Companies across the healthcare ecosystem trust Thoropass

Logo Blackbird.ai
Logo SEMRUSH
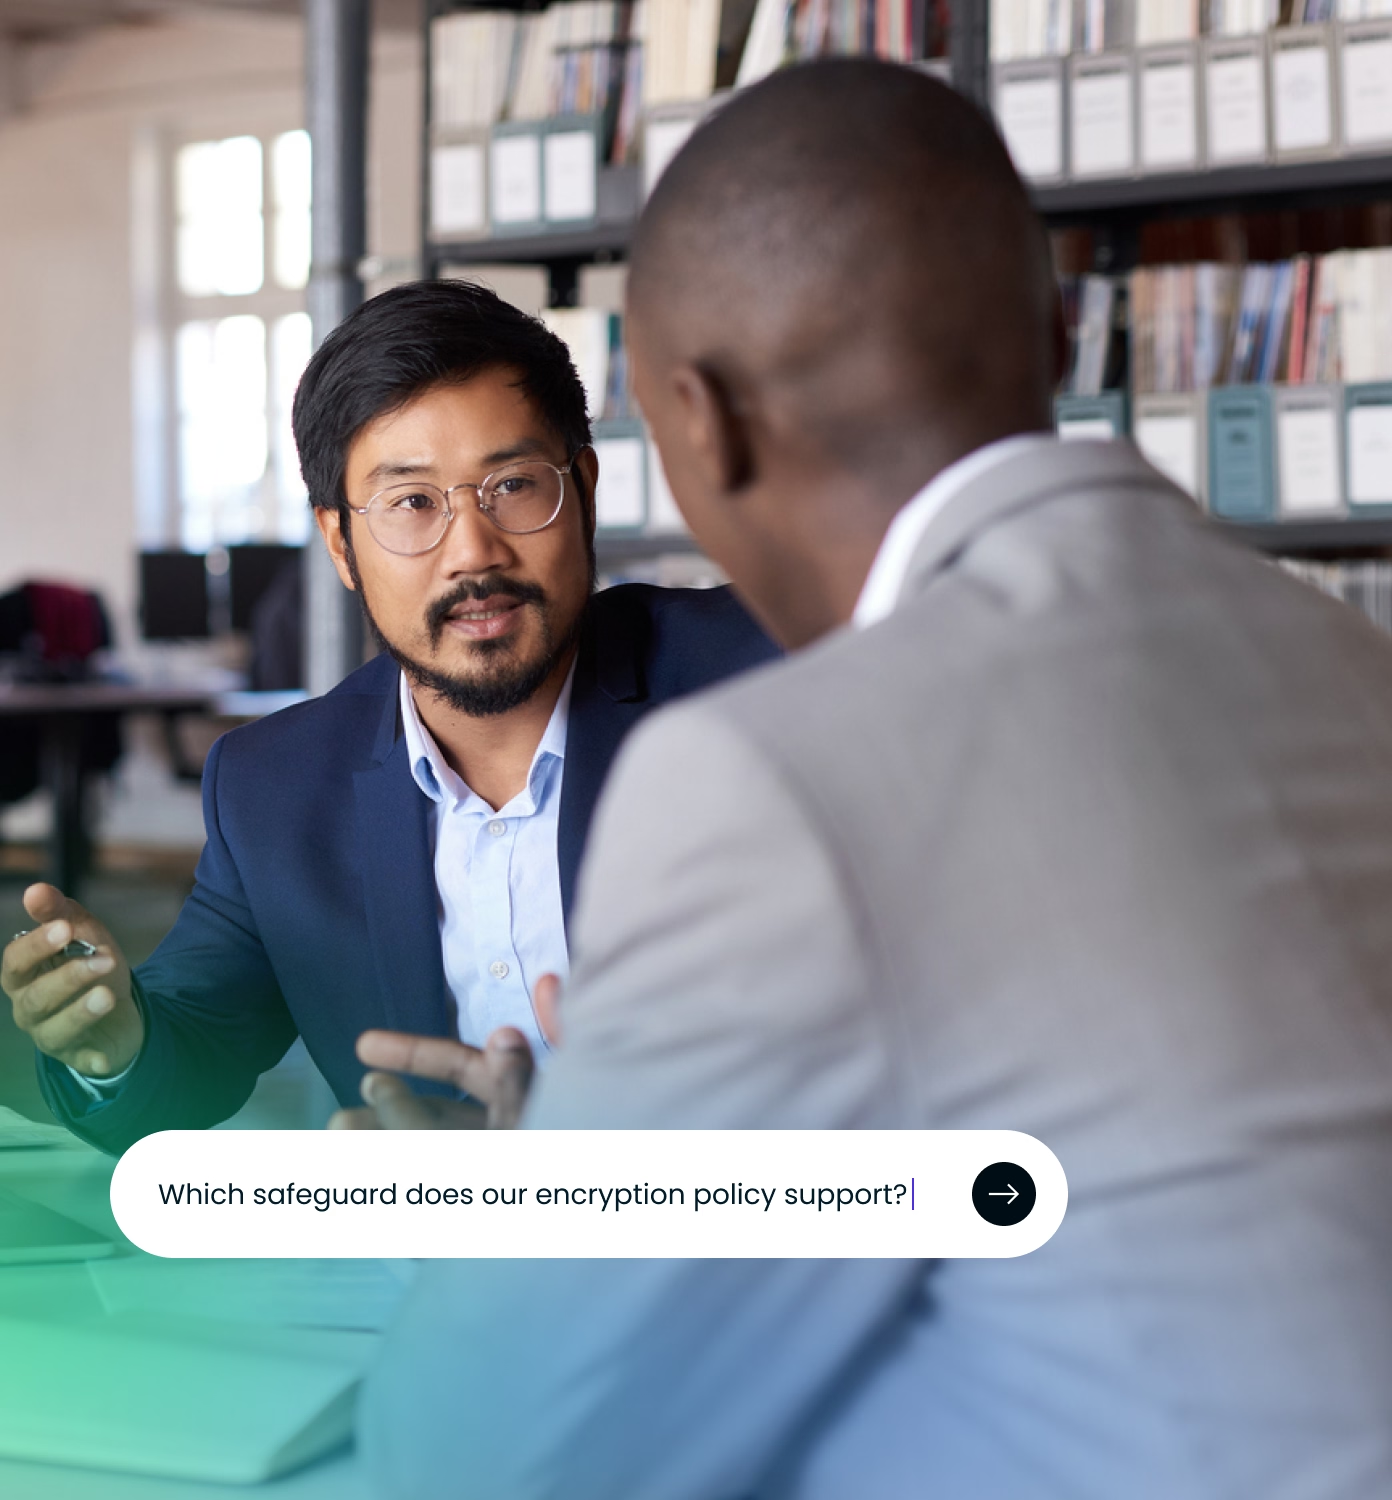
Two men in business attire having a discussion in an office with bookshelves in the background, with a text overlay displaying a query about encryption policy safeguards.
Notification interface on a gradient pink and orange background shows a message: 'A training record changed. Review it before it becomes an audit finding.' with a document icon marked by an exclamation symbol and a 'Review now' button, indicating an audit readiness alert.
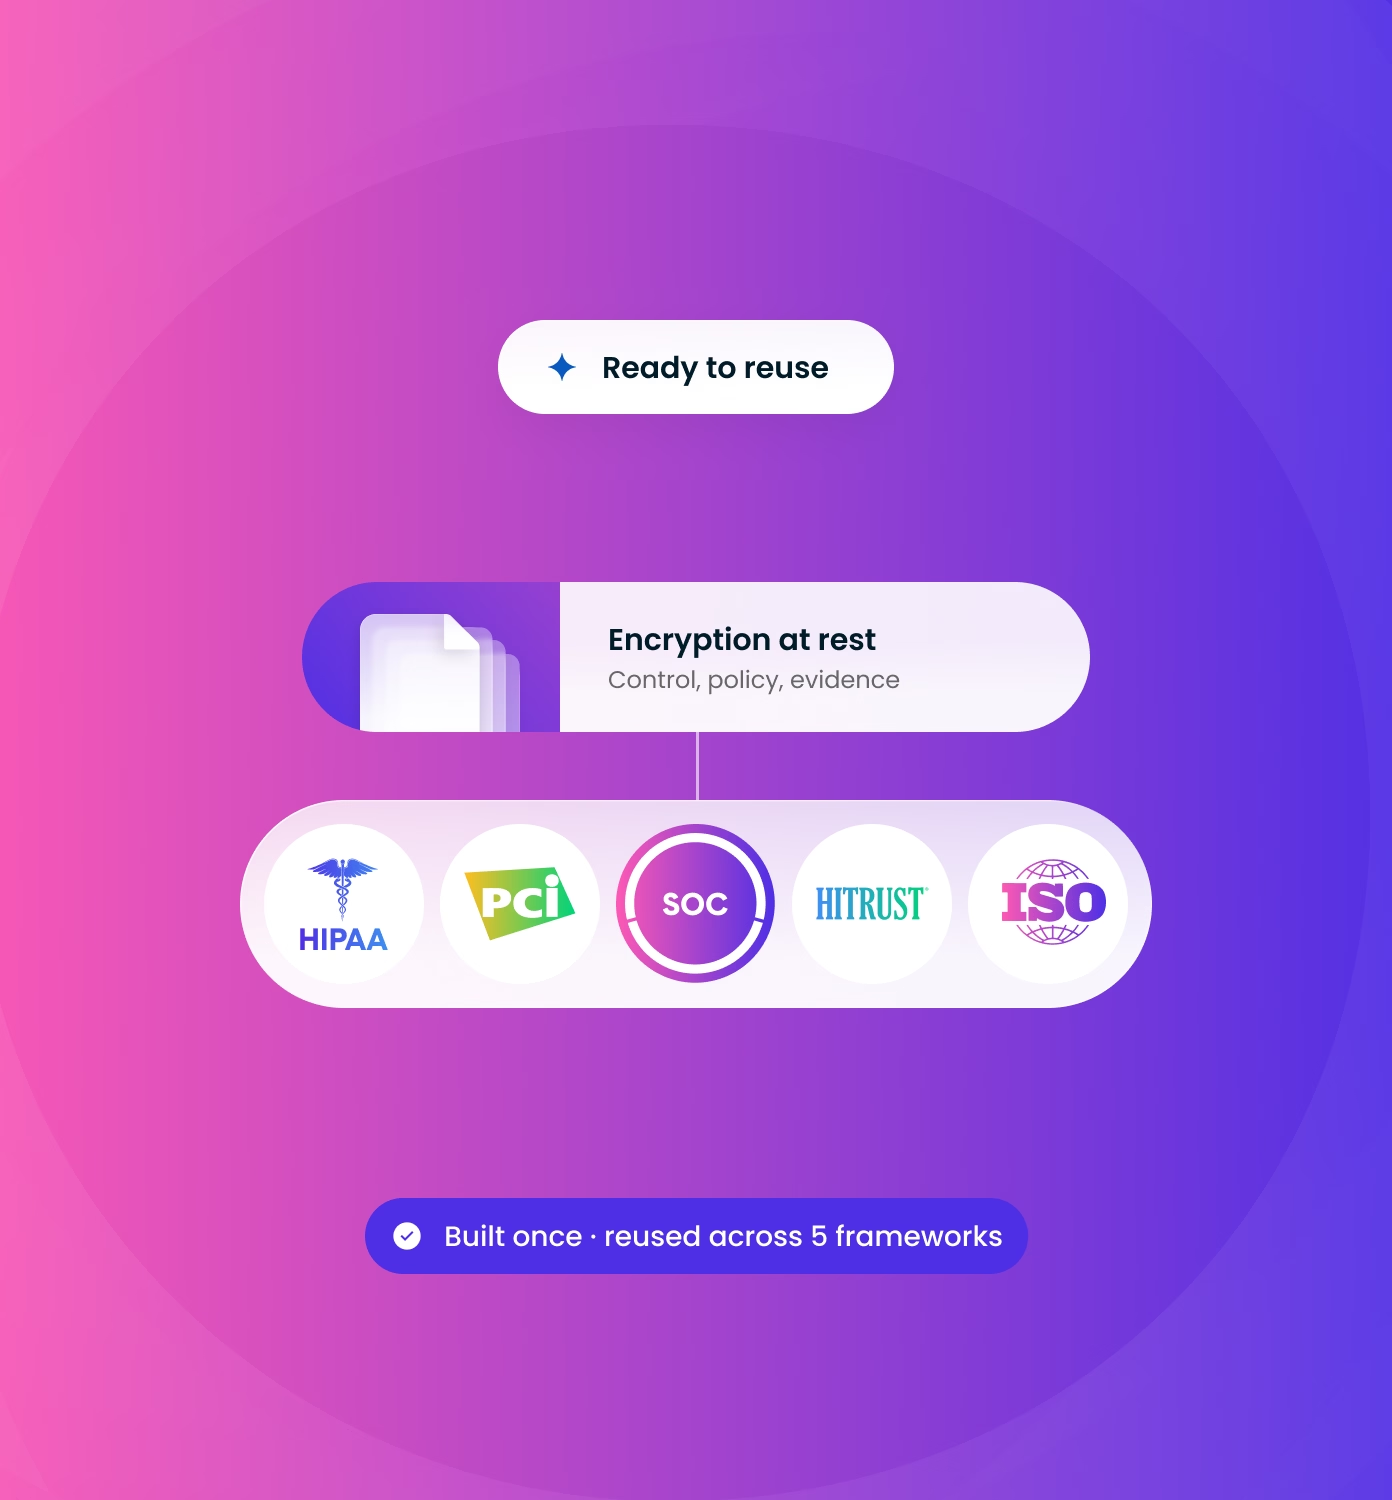
Diagram showing data security concept with a label 'Ready to reuse', highlighting 'Encryption at rest' with control, policy, and evidence, connected to five compliance frameworks: HIPAA, PCI, SOC, HITRUST, and ISO, and a note stating 'Built once · reused across 5 frameworks.'

Achieving HIPAA attestation with Thoropass

Kick-off

After a technical deep dive, Thoropass experts help define the scope of your HIPAA assessment, understand your environment, and identify the teams, systems, policies, and safeguards that need to be reviewed.

Onboarding

Your team starts with a clear assessment plan, practical next steps, and visibility into the work ahead. Thoropass helps align stakeholders early so everyone understands evidence needs, timelines, and responsibilities.

Assessment preparation

Thoropass helps your team prepare for review by organizing key documentation, evidence, risk analysis materials, policies, procedures, and training records. Expert guidance helps reduce confusion and gives your team a more practical path through the assessment.

HIPAA assessment

Thoropass performs a third-party assessment of the safeguards and practices in scope, including how your organization protects PHI and ePHI. Requests, evidence, comments, issues, and status updates are managed through Thoropass's audit lifecycle platform, giving your team and assessor one connected view of progress.

Attestation delivery

At the end of the assessment, Thoropass delivers a trusted report and attestation that can be shared with customers, prospects, and partners. Your team gets clearer evidence of the privacy and security practices that support healthcare trust.

Let’s talk audit

Whether you are pursuing your first HIPAA assessment or looking for a better way to support customer assurance requests, Thoropass can help you complete the process with expert guidance, structured review, and a shareable third-party report.

Better audits, powered by AI and expert auditors

TN Outsourcing

Thoropass has significantly streamlined our HIPAA compliance tasks.”

The platform automates many of the manual processes and provides clear, easy-to-follow workflows, reducing the time and effort required from our team.

Product

HIPAA

Industry

Contact Center

Company size

501-1000

Location

Uruguay

Frequently asked questions

Who needs a HIPAA assessment?

Organizations that create, receive, maintain, transmit, or access protected health information may need to evaluate how their privacy and security practices align with HIPAA. This commonly includes covered entities, such as healthcare providers, health plans, and healthcare clearinghouses, as well as business associates that support covered entities and handle PHI.

What is Protected Health Information (PHI)?

Protected Health Information, or PHI, is individually identifiable health information created, received, maintained, or transmitted by a covered entity or business associate. PHI can include information related to a person's health condition, care, payment for care, or other identifiers connected to healthcare services.

What is ePHI?

Electronic Protected Health Information, or ePHI, is PHI that is created, received, maintained, or transmitted electronically. The HIPAA Security Rule focuses on protecting ePHI through administrative, physical, and technical safeguards.

What does a HIPAA assessment review?

A HIPAA assessment reviews the safeguards, policies, procedures, documentation, and practices your organization uses to protect PHI and ePHI. This can include areas such as risk analysis, access controls, workforce training, incident response, business associate management, audit trails, and physical and technical safeguards.

What is the difference between the HIPAA Privacy Rule and Security Rule?

The HIPAA Privacy Rule addresses how PHI can be used and disclosed and gives individuals rights related to their health information. The HIPAA Security Rule focuses on protecting ePHI and requires regulated entities to use administrative, physical, and technical safeguards to support the confidentiality, integrity, and availability of that information.

What is a HIPAA incident response plan?

A HIPAA incident response plan outlines how an organization identifies, investigates, responds to, and documents potential security incidents involving PHI or ePHI. A clear plan helps teams respond more consistently, reduce the impact of incidents, and support breach notification analysis when needed.

What are the benefits of working with Thoropass for a HIPAA assessment?

Thoropass combines experienced assessors, a structured assessment process, and an audit lifecycle platform to help teams manage the HIPAA assessment from kickoff through attestation delivery. Your team gets clearer requests, organized evidence review, expert guidance, and a shareable third-party report for customers and partners.