SOC 2, with the auditor built into the experience

SOC 2 gives customers independent assurance in your security controls. Thoropass combines AI-native capabilities and expert auditors in one connected experience to reduce audit overhead and help you build trust faster.

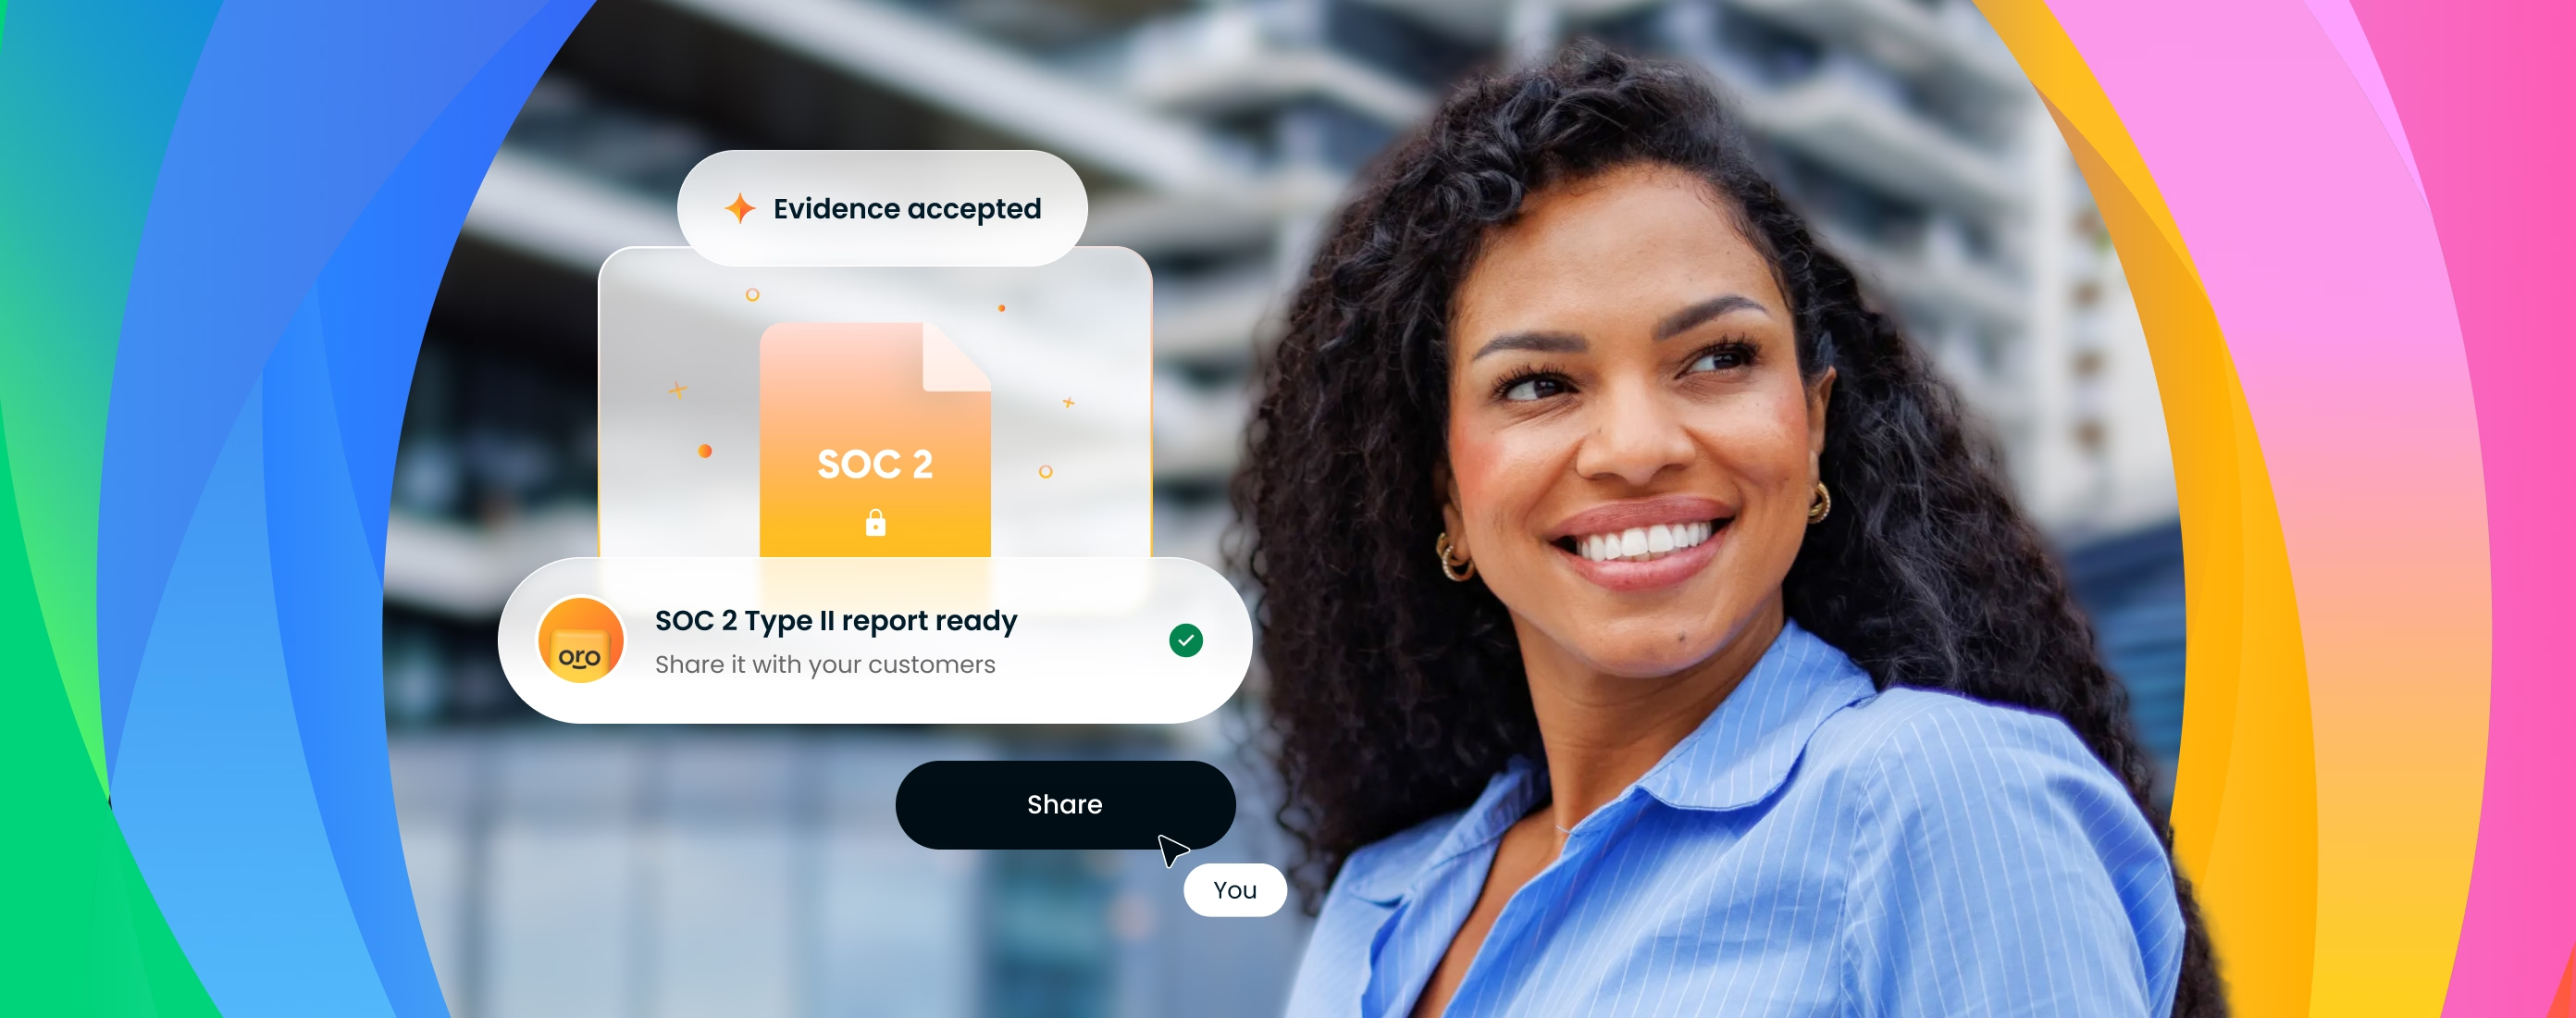
Smiling woman with curly hair in a blue blouse on right side, with an overlay graphic on the left showing a document labeled SOC 2, text stating 'Evidence accepted', 'SOC 2 Type II report ready', and a black button labeled 'Share'.

Logo Blackbird.ai
Logo SEMRUSH
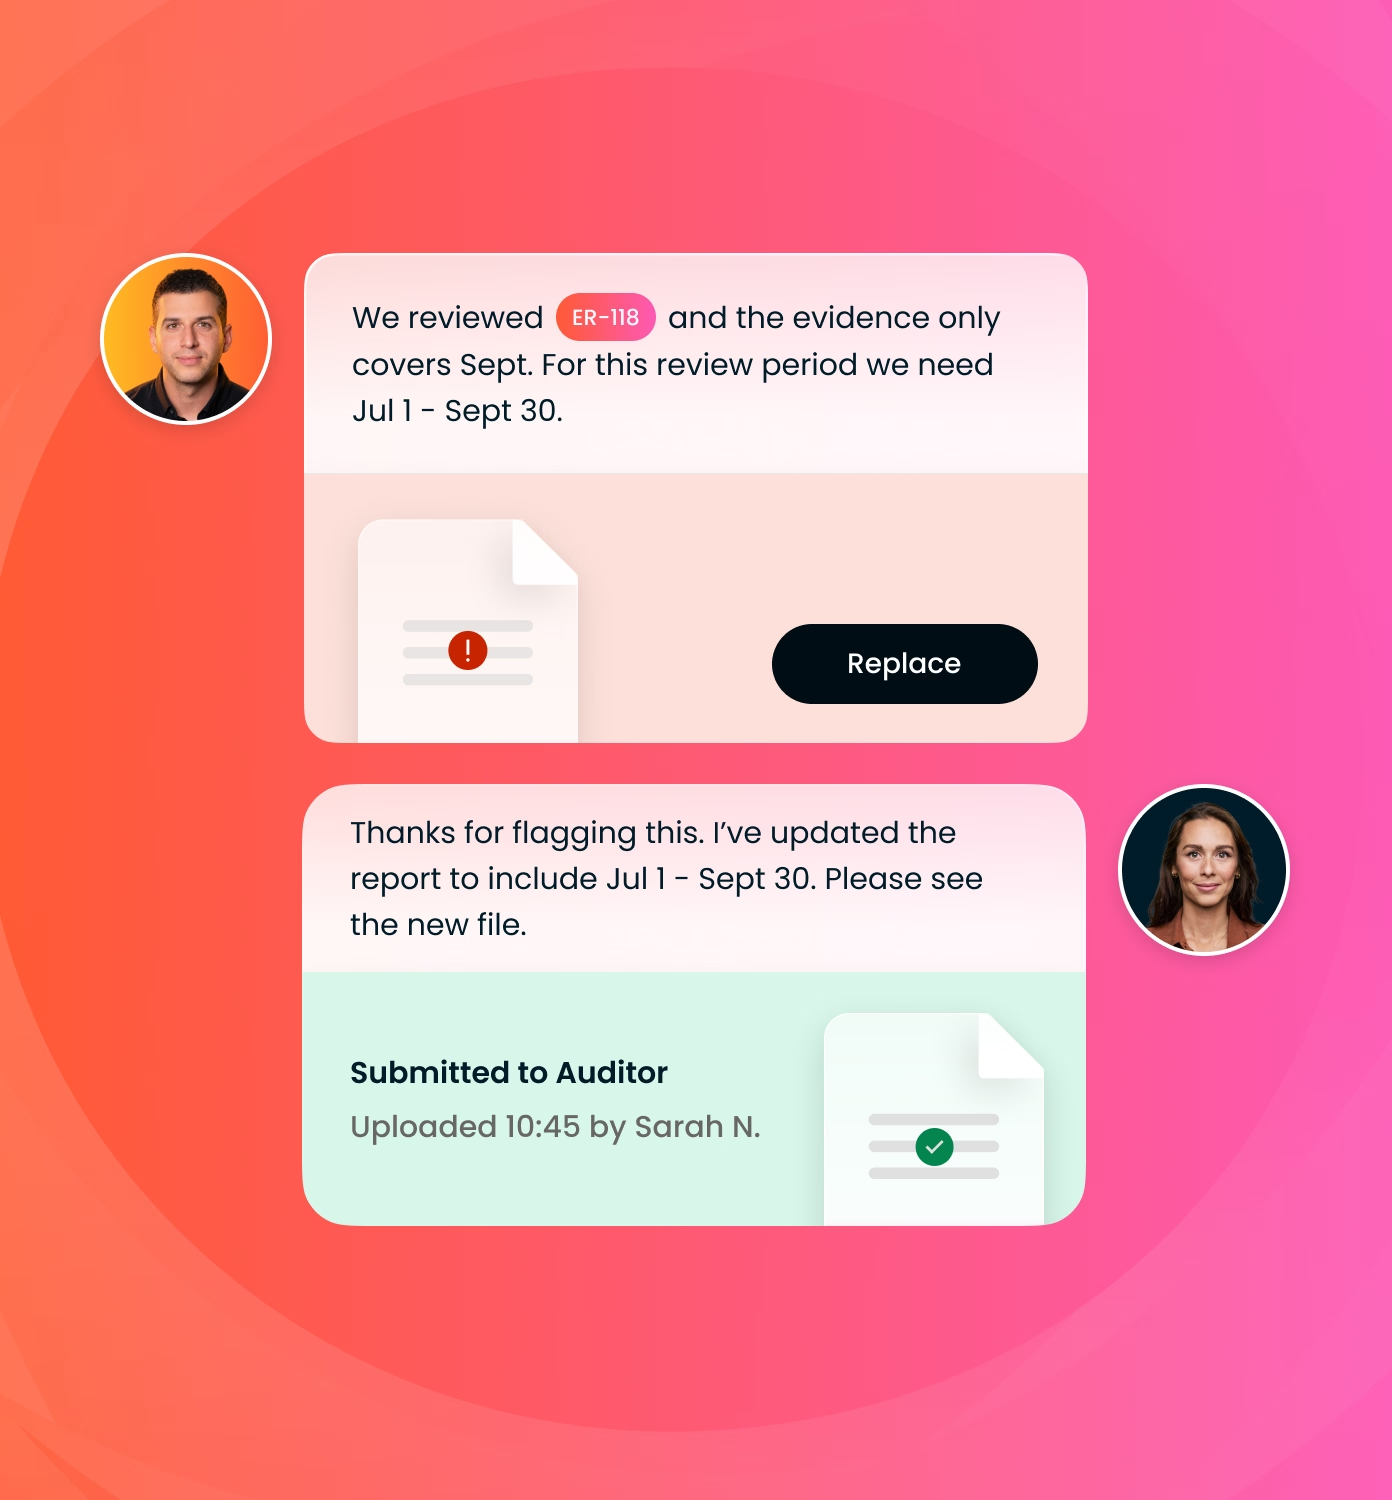
Chat conversation between two people about document review, with a male avatar on the left and female avatar on the right. The man says the evidence covers only September and requests files for July 1 to September 30, showing a file icon with an error symbol and a Replace button. The woman replies that she updated the report and uploaded the new file at 10:45, showing a file icon with a checkmark and a Submitted to Auditor label.
Smiling woman with curly hair wearing a white shirt and light jacket looking at a laptop, with overlay text showing a progress status reading 'Auditor review in progress' and 'AI checks complete' with checkmark.
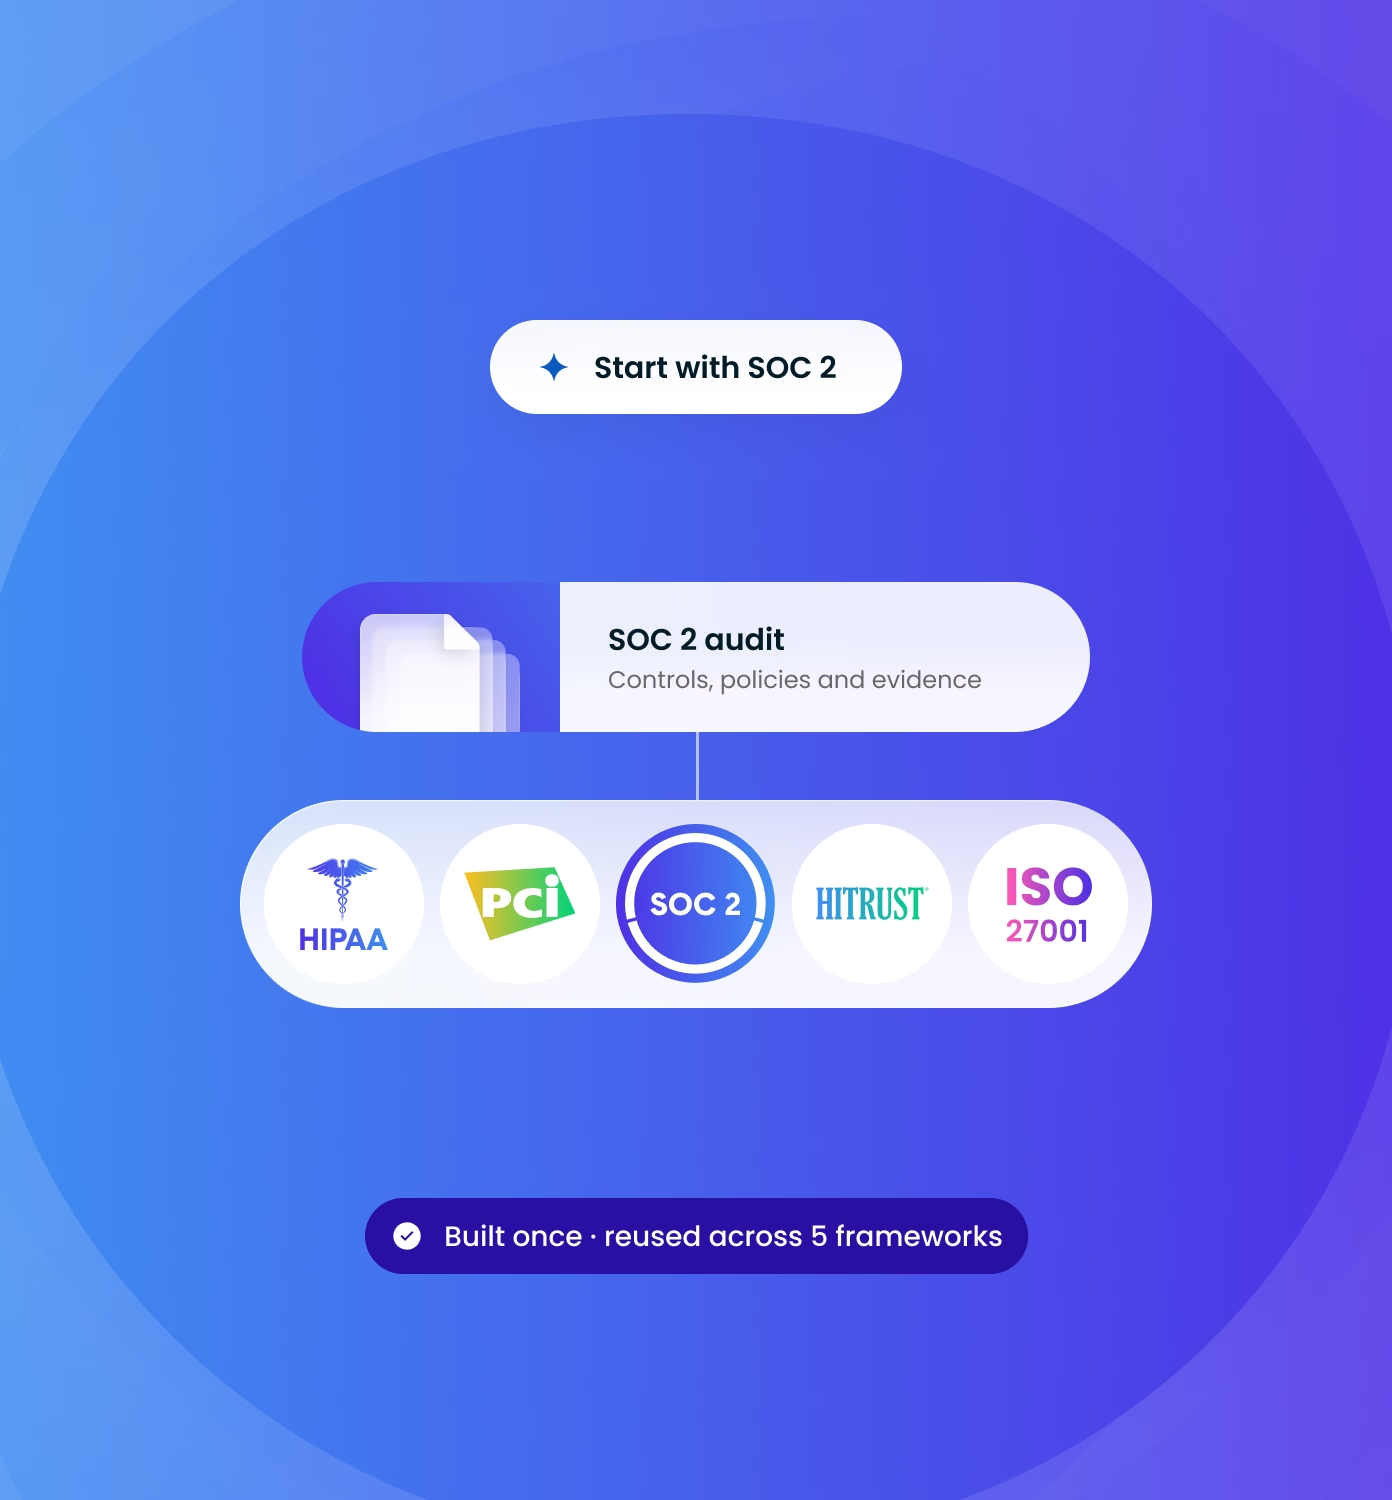
Diagram showing SOC 2 audit as a central document representing controls, policies, and evidence, connected to five compliance frameworks: HIPAA, PCI, SOC 2, HITRUST, and ISO 27001, with a button labeled 'Start with SOC 2' and a note below stating 'Built once · reused across 5 frameworks' on a blue gradient background.
Smiling man with curly hair and beard wearing a light blue shirt, with text overlays showing source icons for AWS, Slack, and GitHub and a checklist with items: Access reviews, Change management, and Vendor risk, each marked with a check.

Better audits, powered by AI and expert auditors

all-in-one

We were unhappy with the previous provider that we picked for many reasons, but most importantly, it was the auditor and the platform being separate.”

With its holistic approach to security and compliance, a seamless platform, and hands-on support, Thoropass was the partner Opstream needed.

Product

SOC 2

Industry

B2B Software, Procurement

Company size

11-50

Location

United States

seamless experience

With Thoropass’s seamless audit experience, we were able to get the audit done in a fraction of the time.

Capitalize CTO Chris Phillips could work with any auditor, but chose Thoropass because of its exclusive inclusion of in-house expertise.

Product

SOC 2

Industry

Fintech

Company size

50-100

Location

United States

frictionless compliance

The audit process was absolutely painless, and Thoropass made our three weeks less of a headache.

Wayleadr chose Thoropass as their trusted compliance platform due to the closed-loop solution of powerful software and human expertise.

Product

SOC 2

Industry

Software Development

Company size

26-50

Location

Ireland, United States

growth through quality support

If my previous audits were offered to me for free, I would still use Thoropass

Stylo’s co-founder and CTO Josh Horowitz enjoyed exponential growth after enjoying his audit and support experience with Thoropass.

Product

SOC 2

Industry

Artificial Intelligence, Computer Software

Company size

26-50

Location

United States

Start your audit
with Thoropass

Streamline your operations and build trust with customers by working toward SOC 1 compliance with Thoropass.

Everything you need to know to leverage it for your business

From best practices to guides to checklists, we have you covered.

Meet your audit experts

Frequently asked questions

What is SOC 2?

SOC 2 is an independent audit report that evaluates whether a service organization has controls in place to protect customer data. It is commonly requested of SaaS, technology, and cloud-based companies because it helps customers assess how an organization manages security, availability, confidentiality, processing integrity, and privacy.

What is SOC 2 Type I vs. SOC 2 Type II

A SOC 2 Type I audit evaluates the design of controls at a specific point in time. It helps show whether the right controls are in place as of the report date.

A SOC 2 Type II audit evaluates both the design and operating effectiveness of controls over a review period, often 3 to 12 months. It helps show whether controls are not only designed appropriately, but also operating consistently over time.

What is the difference between SOC 1, 2, and 3?

SOC 1 evaluates controls that could impact a customer's financial reporting. It is primarily intended for organizations such as payroll providers, payment processors, and financial service providers whose services affect their customers' financial statements.

SOC 2 assesses an organization's controls for protecting customer data based on the Trust Services Criteria. It is the most widely requested audit for B2B SaaS and technology companies.

SOC 3 is a public-facing summary of a successful SOC 2 audit. It confirms that an organization has met the applicable Trust Services Criteria without including the detailed control descriptions and testing results found in a SOC 2 report, making it suitable for websites and marketing materials.

What are controls?

Controls are the policies, procedures, systems, and activities an organization uses to reduce risk and meet audit criteria. In a SOC 2 audit, controls are evaluated against the Trust Services Criteria included in the audit scope.

What are the Trust Services Criteria (TSA)?

The Trust Services Criteria are the categories used to evaluate controls in a SOC 2 audit. They include Security, Availability, Confidentiality, Privacy, and Processing Integrity. Every SOC 2 audit includes Security, and additional criteria may be added based on customer requirements and business needs.

How much does SOC 2 cost?

SOC 2 audit costs vary based on scope, company size, systems included, Trust Services Criteria, audit type, and the length of the review period. Thoropass helps make the process more predictable by defining scope early, managing the audit lifecycle in one place, and guiding the engagement through final report delivery.

What are the benefits of SOC 2 auditor like Thoropass?

Working with Thoropass gives your team access to experienced SOC 2 auditors equipped with proprietary AI tools that automate repetitive tasks, accelerate evidence review, and surface insights throughout the audit. Combined with our Audit Lifecycle Platform for managing requests, evidence, comments, issues, and reporting, you get a faster, more transparent audit experience without compromising quality or rigor.

What does ongoing SOC 2 audit readiness mean?

Ongoing SOC 2 audit readiness means keeping the controls, documentation, and evidence needed for future SOC 2 audits organized and current. For Type II audits in particular, organizations need to show that controls operated effectively over the review period, so consistent preparation can make future audit cycles more efficient.