Audit-ready
financial reporting

Demonstrate that the controls supporting your customers’ financial reporting are designed and operating effectively. Thoropass combines readiness, evidence collection, and audit into one connected experience, helping you streamline every step from scoping to your final report.
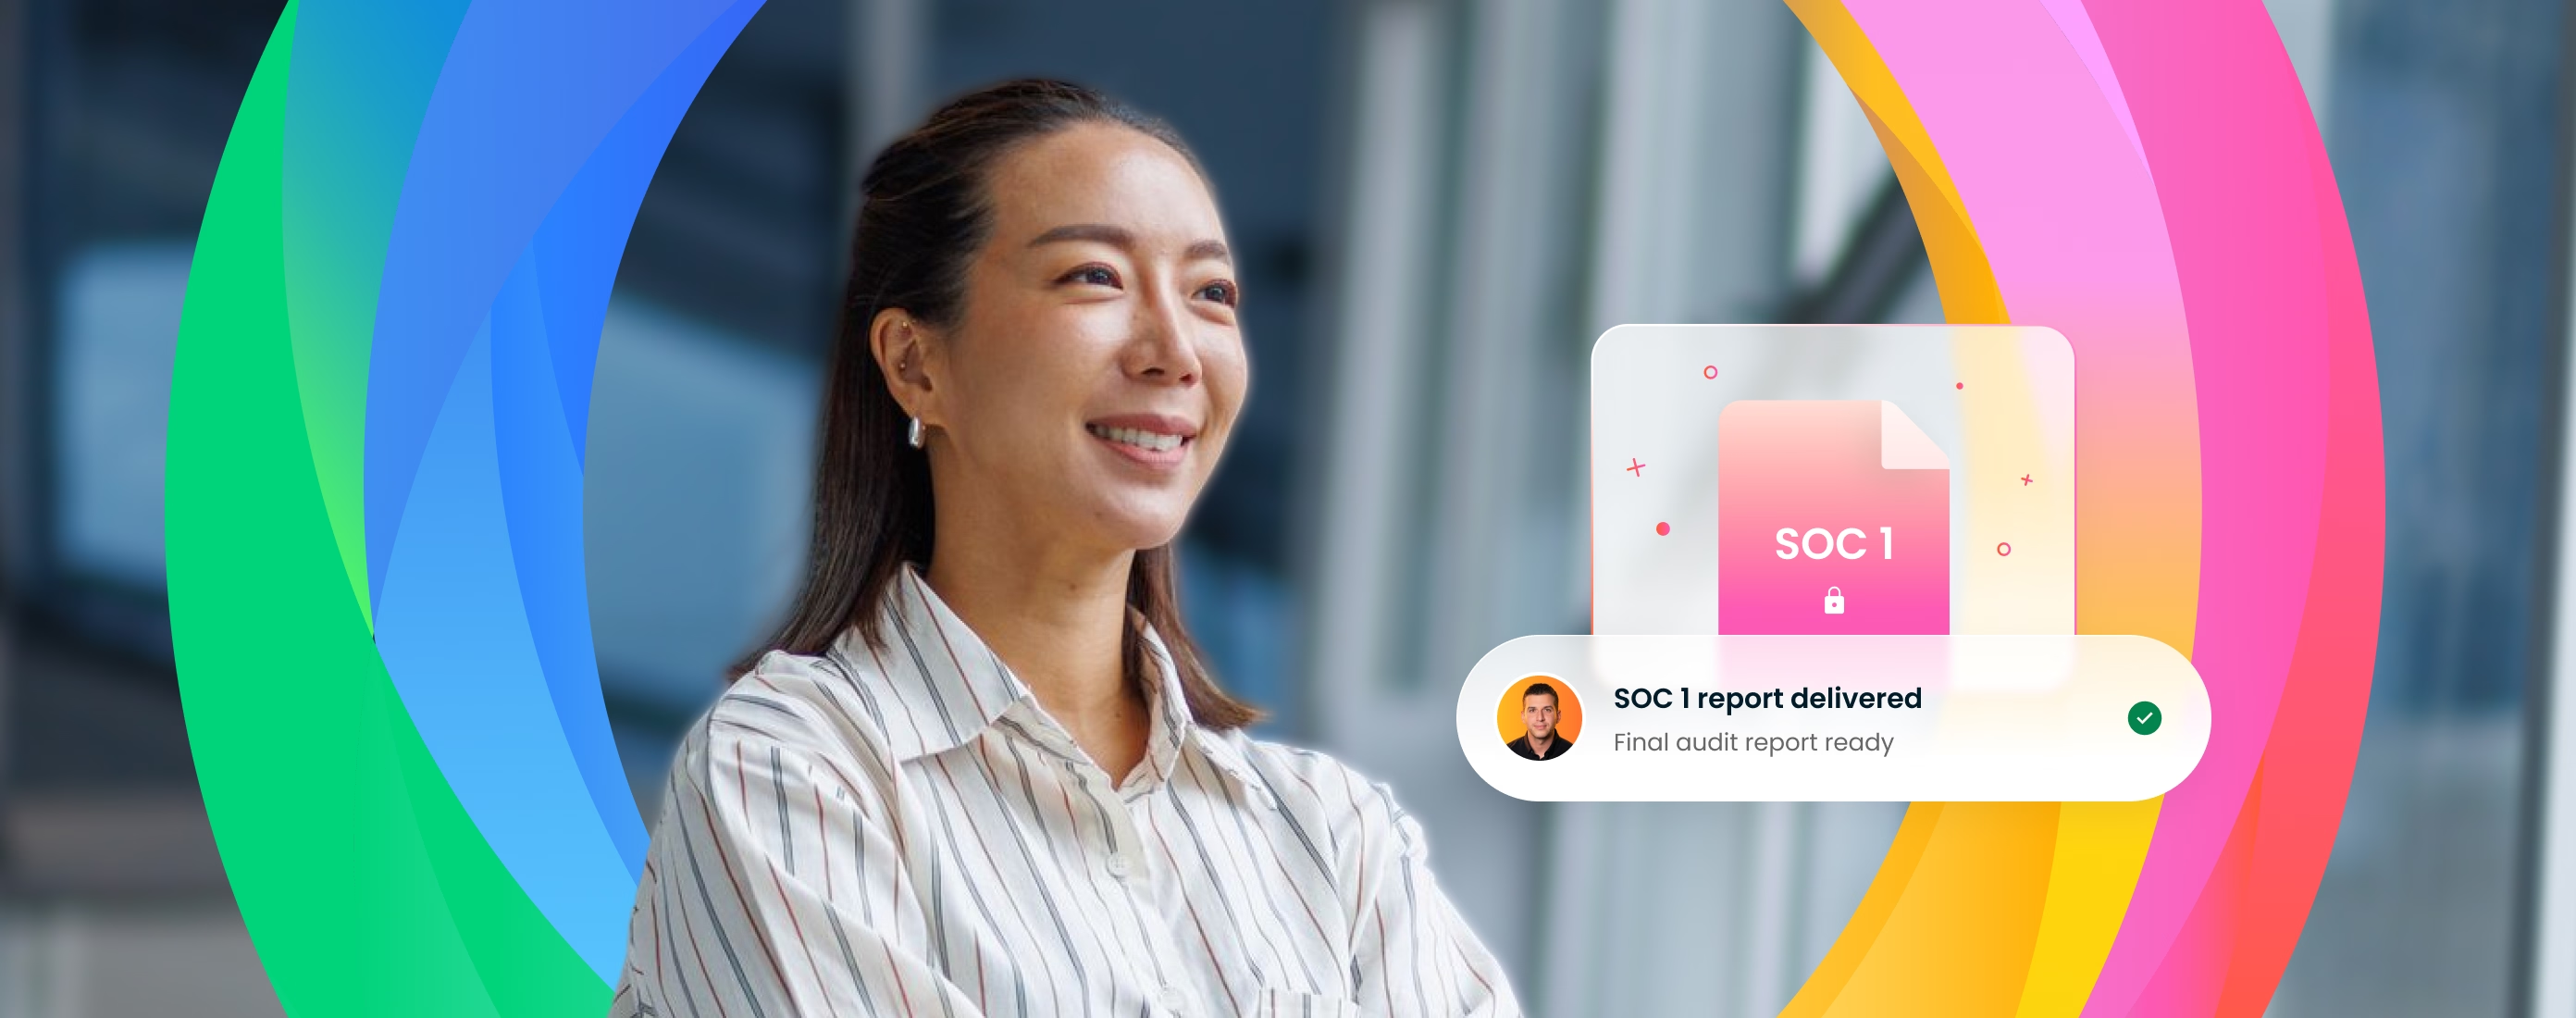
Smiling woman with long dark hair in a striped white shirt standing in an office, framed by colorful curved bands. A locked SOC 1 document icon sits above a card reading 'SOC 1 report delivered: Final audit report ready' with an auditor avatar and a green check.
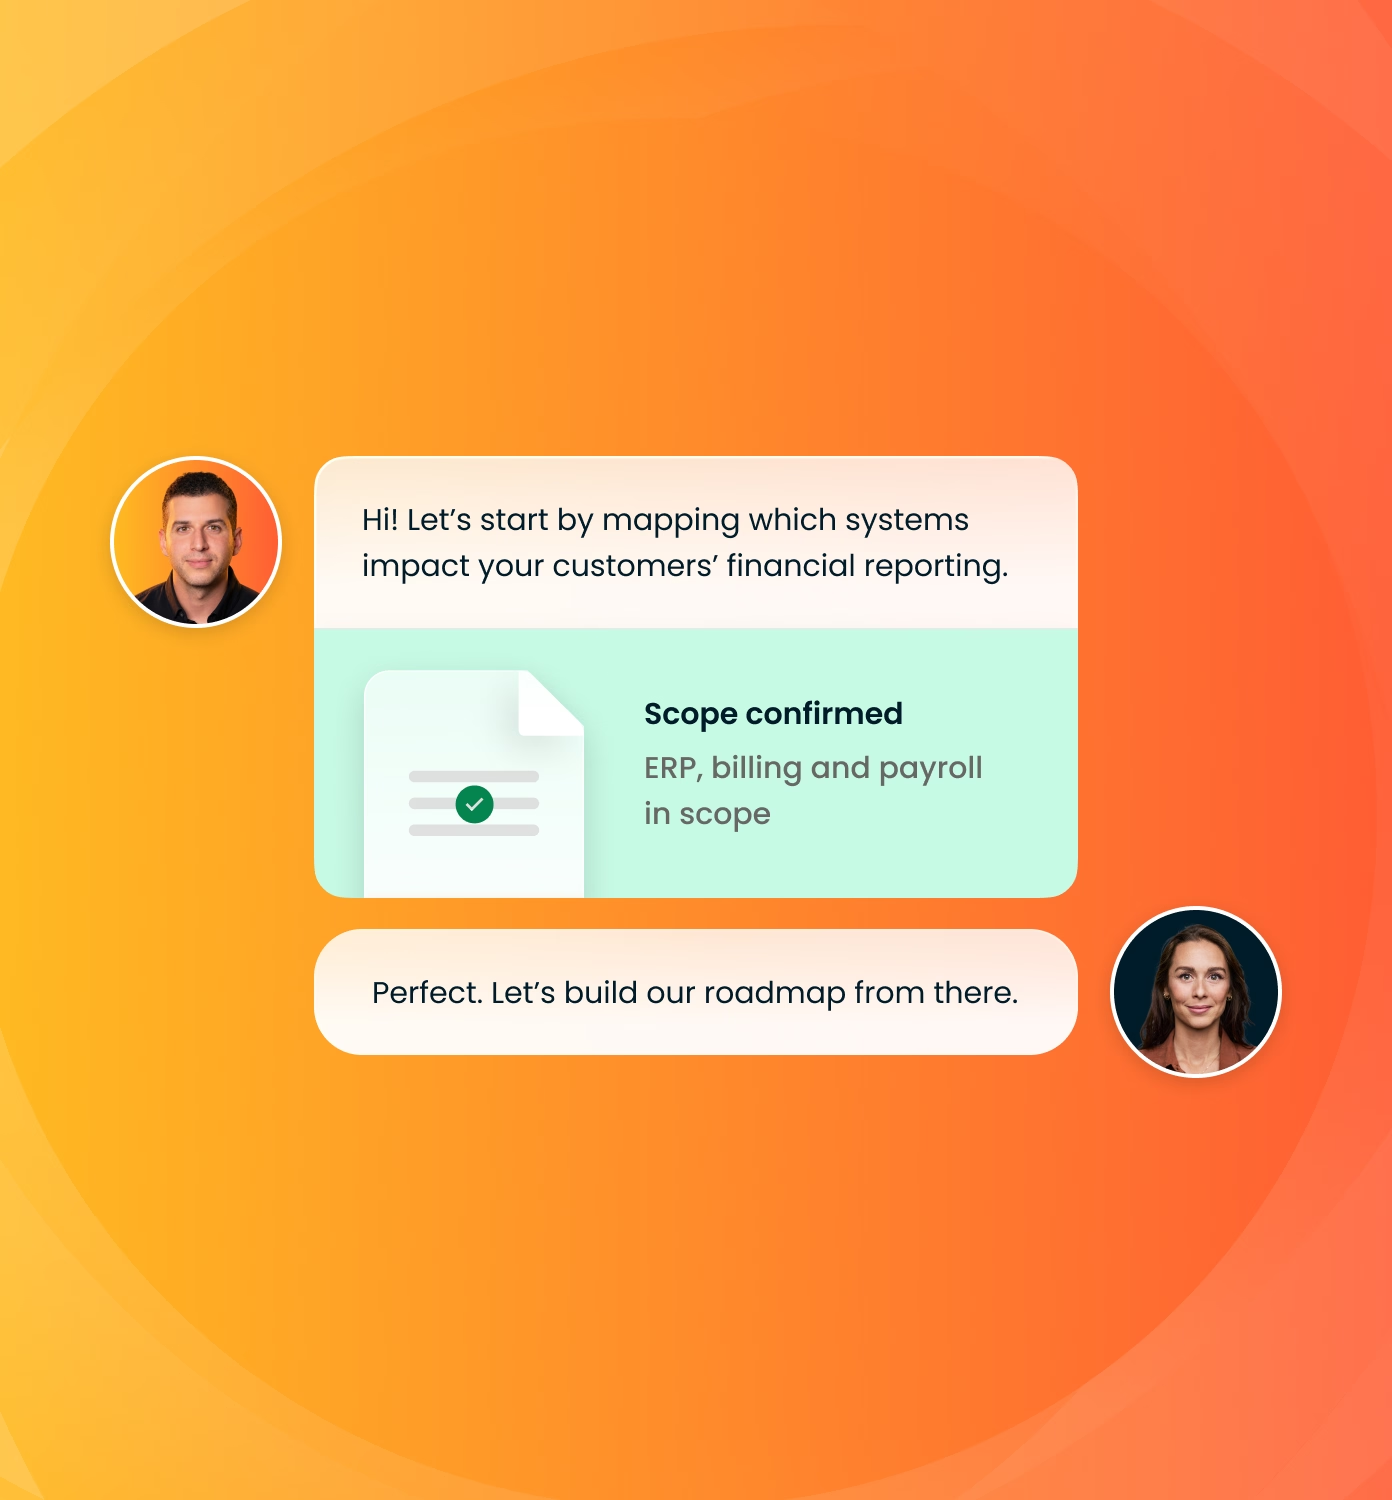
Chat interface with two people communicating about financial reporting systems; one says, 'Hi! Let's start by mapping which systems impact your customers' financial reporting.' A confirmation card says, 'Scope confirmed: ERP, billing and payroll in scope.' The other responds, 'Perfect. Let's build our roadmap from there.'
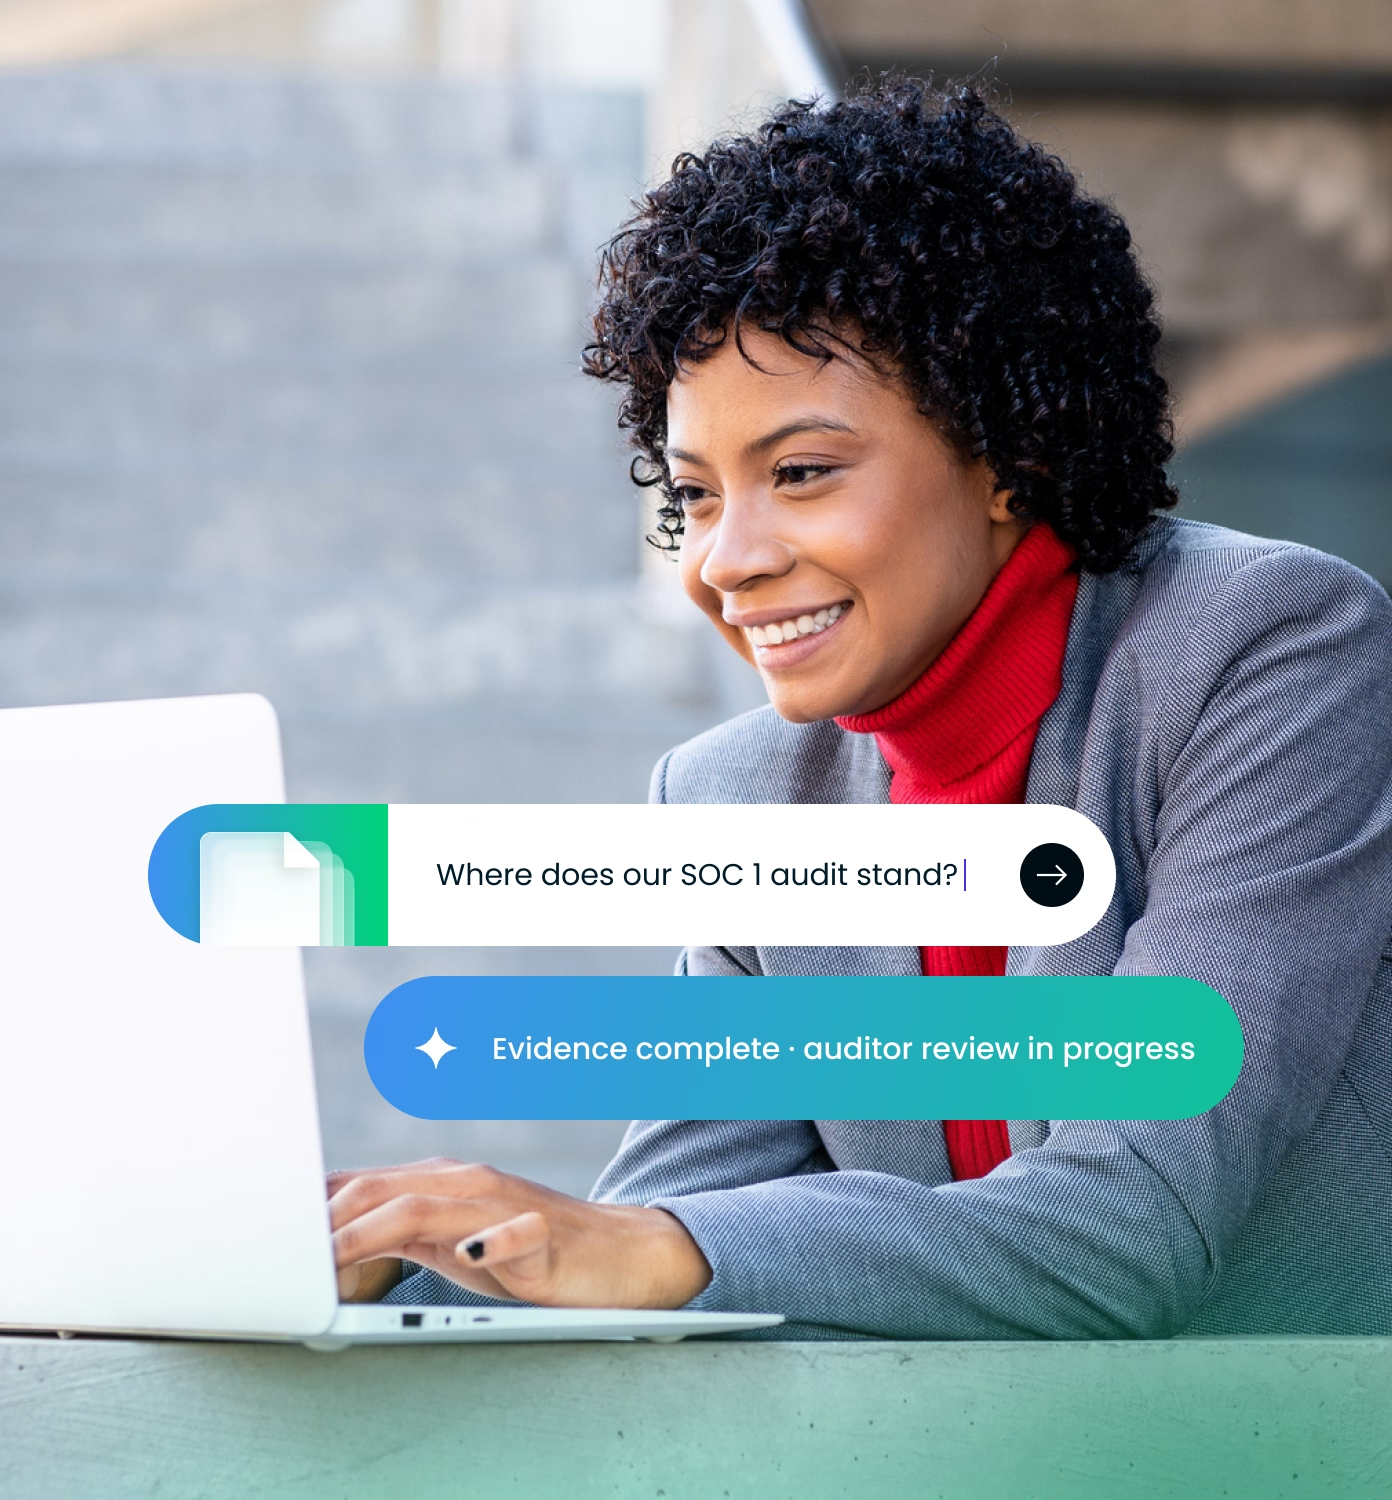
Smiling woman with curly hair wearing a gray blazer and red turtleneck, working on a laptop outdoors, with on-screen text prompts about SOC 1 audit status and evidence completion.
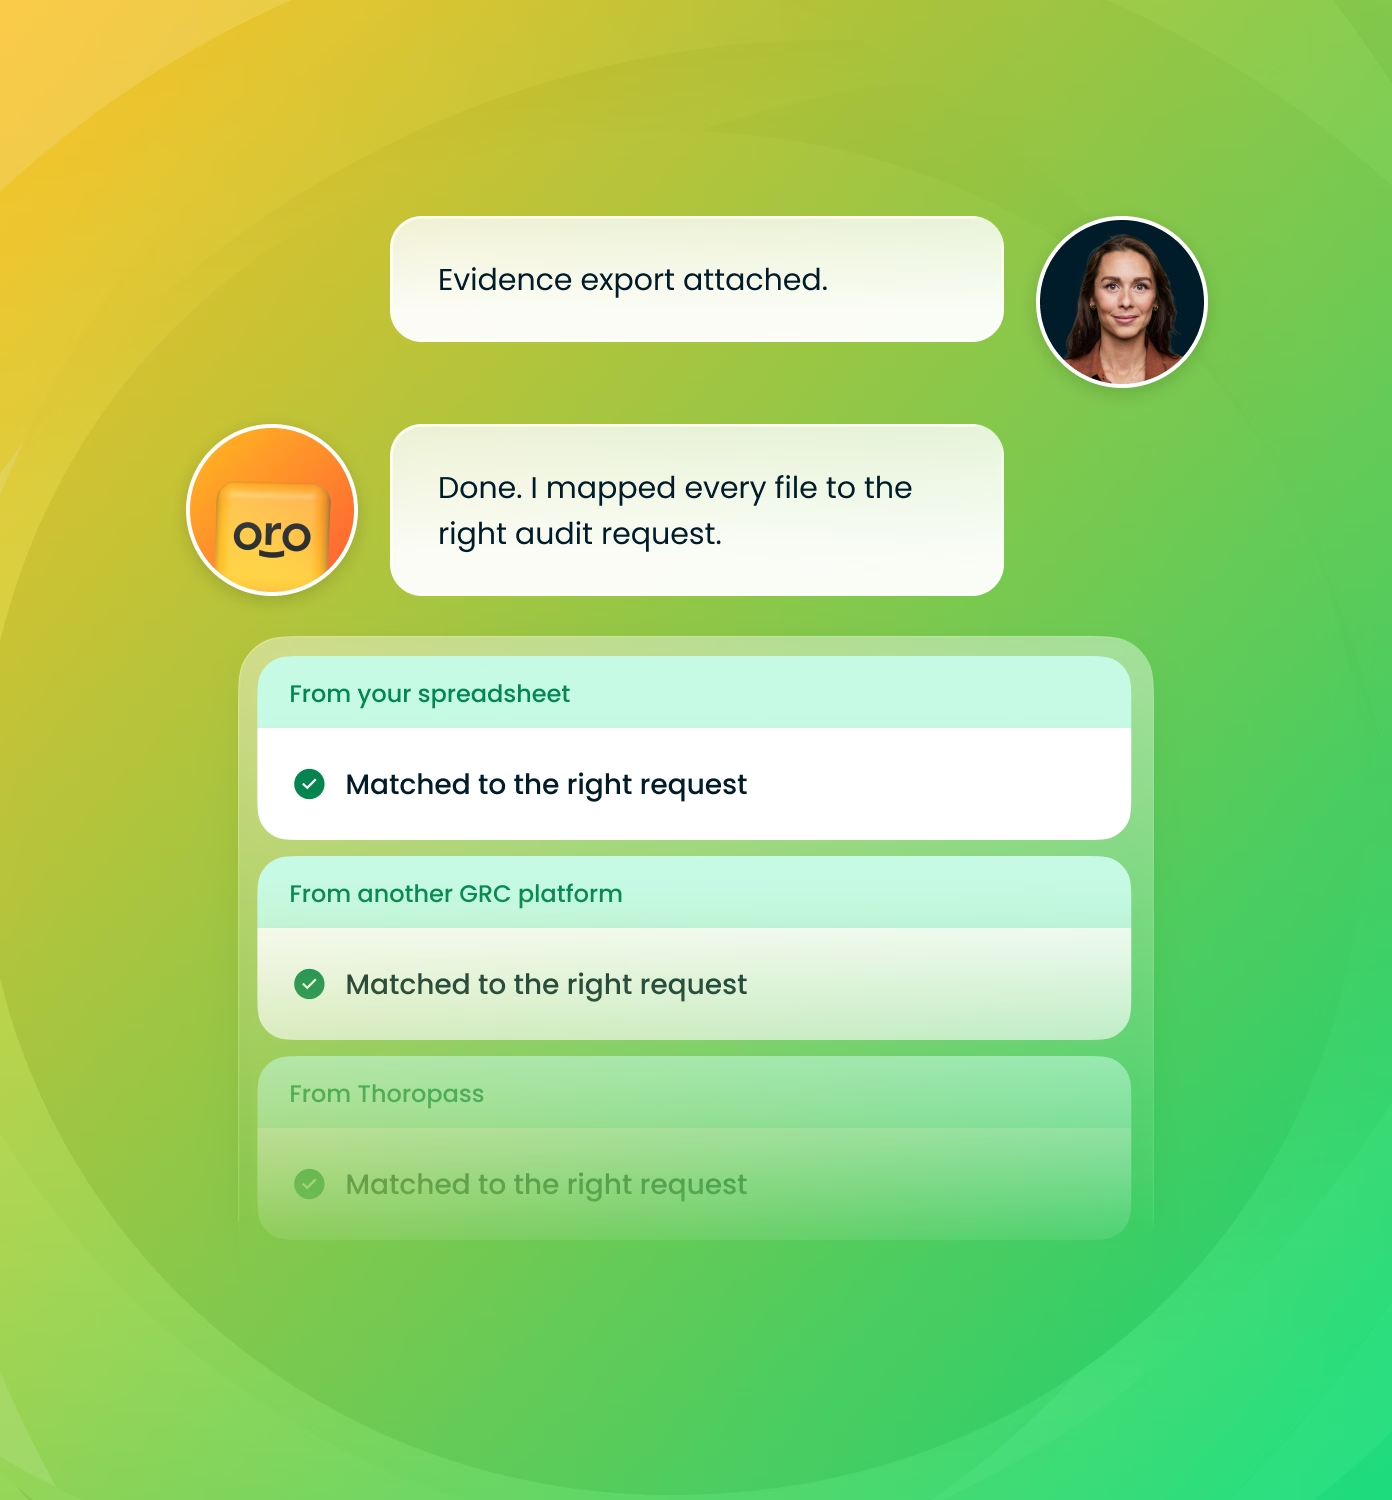
Chat interface on a green-yellow gradient background showing a conversation where a user with a female profile picture says 'Evidence export attached,' and a user with an orange logo replies 'Done. I mapped every file to the right audit request.' Below are three status boxes: 'From your spreadsheet' and 'From another GRC platform' both show a green check and 'Matched to the right request,' while 'From Thoropass' is faded with a grey check and faded text 'Matched to the right request.'
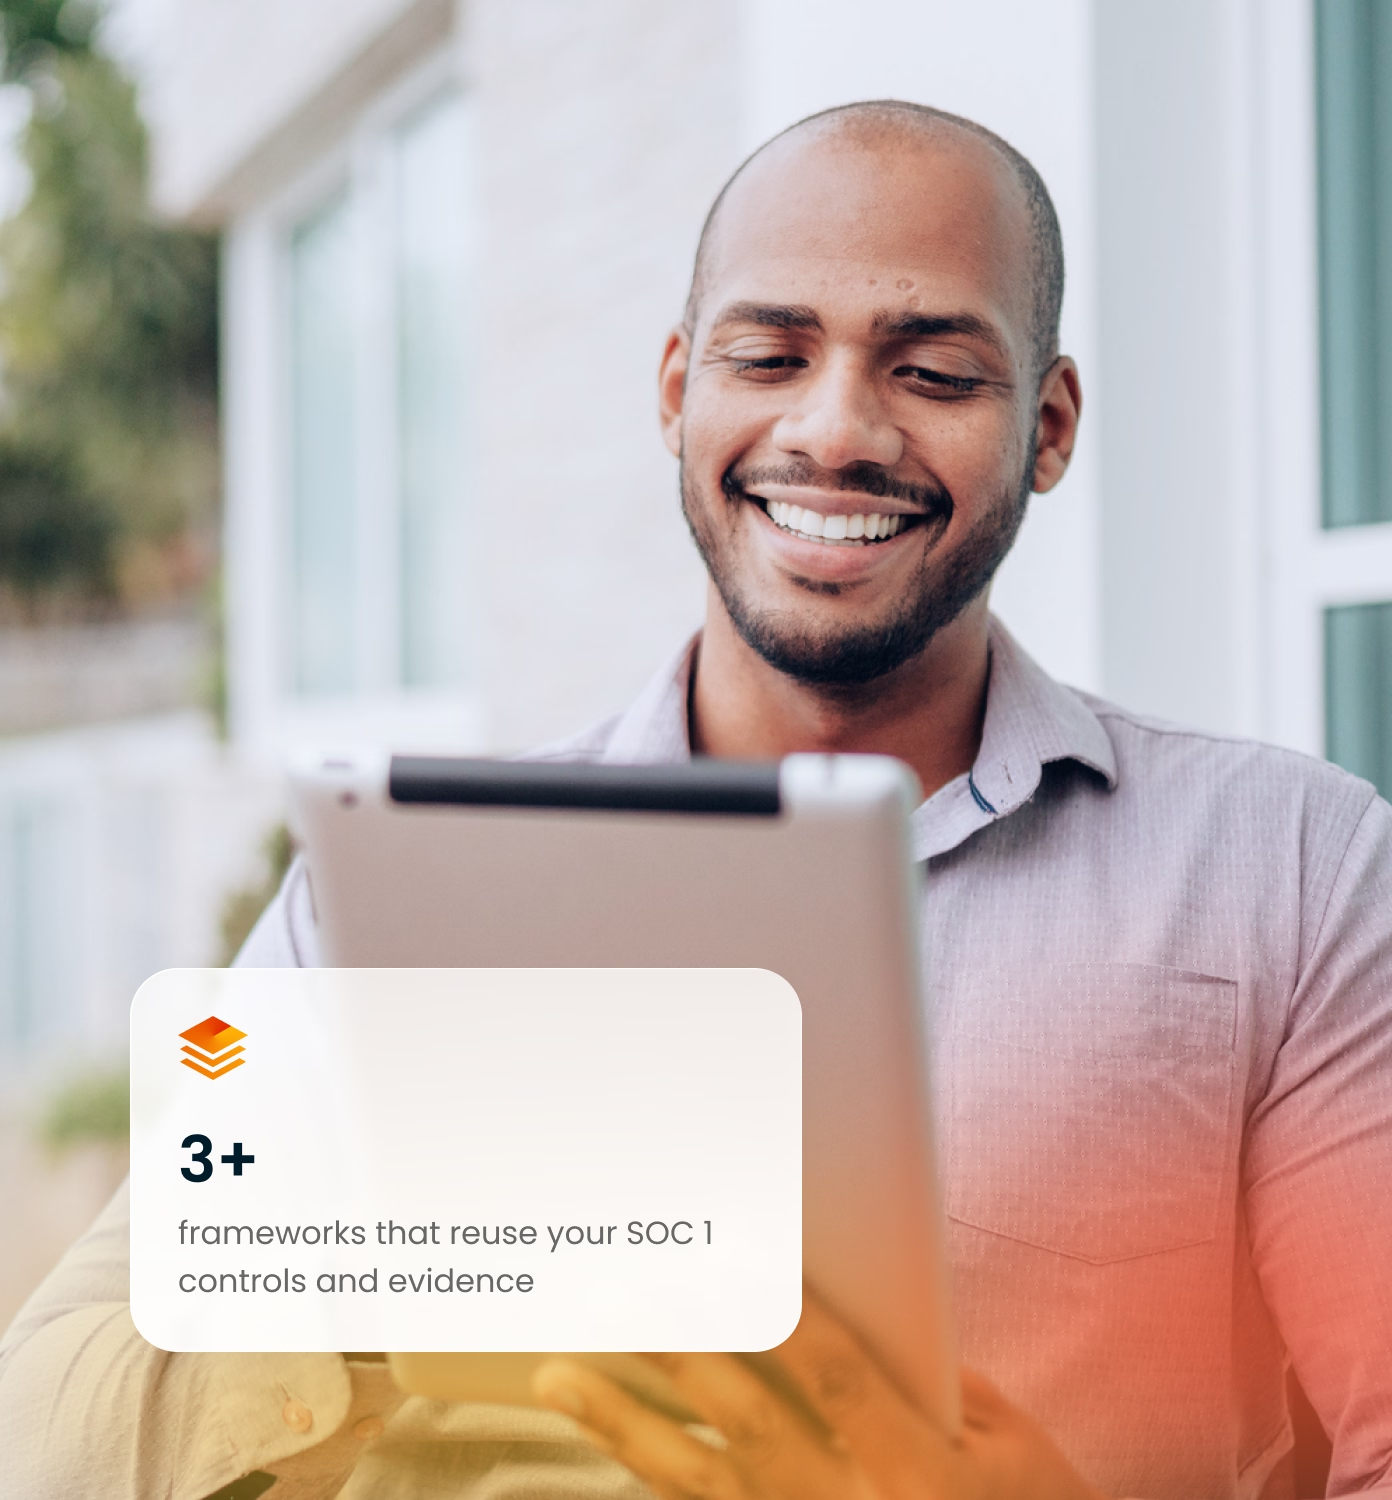
Smiling man with a beard wearing a light purple shirt, sitting outdoors and looking at a tablet he is holding with both hands, with a white text box on the bottom left containing an orange stacked layers icon and the text '3+ frameworks that reuse your SOC 1 controls and evidence'.

Better audits, powered by AI and expert auditors

The Customer Success Managers have been outstanding – guiding us through the process and ensuring we’re always on track.”

This has been one of the highlights of working with Thoropass. The process has been streamlined and clear, and we’ve never felt unprepared or surprised.

Framework

HIPAA, SOC 1, SOC 2

Industry

Fintech

Company size

26-50

Location

United States

A man and a woman in business attire smiling as they look at a tablet the woman is holding in a bright hallway.
5 stars

Our users agree − there’s a better way to do audits.

You don't just have to take our word for it. Our reviews on G2 back up that Thoropass makes audits simpler and drives better outcomes.

Start your journey with Thoropass

Streamline your operations and build trust with customers by working toward SOC 1 compliance with Thoropass.

Frequently asked questions

What is a SOC 1 audit?

A SOC 1 audit evaluates controls at a service organization that may affect its customers’ financial reporting. It is commonly requested when a company provides services that can influence financial transactions, financial data, payroll, billing, claims processing, loan servicing, or other business processes tied to customer financial statements.

Who needs a SOC 1 audit?

Organizations may need a SOC 1 audit when their services affect a customer’s financial reporting or internal controls over financial reporting. This often includes fintech companies, payroll providers, payment processors, benefits administrators, loan servicing platforms, data processors, and other service organizations that support financial operations for customers.

What is the difference between SOC 1 Type I and SOC 1 Type II?

A SOC 1 Type I audit evaluates whether controls are suitably designed at a specific point in time. A SOC 1 Type II audit evaluates both control design and operating effectiveness over a review period, often three to 12 months.

What is the difference between SOC 1 and SOC 2?

SOC 1 focuses on controls that may affect customers’ financial reporting. SOC 2 focuses on controls related to security, availability, processing integrity, confidentiality, and privacy. Customers usually request SOC 1 when they need assurance tied to financial reporting, and SOC 2 when they need assurance tied to how systems and data are protected.

What are controls in a SOC 1 audit?

Controls are the policies, procedures, systems, and activities your organization uses to reduce risk and support reliable service delivery. In a SOC 1 audit, controls are evaluated based on how they support the control objectives included in the audit scope.

How long does a SOC 1 audit take?

SOC 1 audit timelines vary based on audit scope, control complexity, evidence readiness, number of stakeholders, and whether you are pursuing a Type I or Type II report. Thoropass helps make the process more predictable by defining scope early, organizing requests and evidence in one audit lifecycle platform, and guiding the engagement through final report delivery.

What are the benefits of working with a SOC 1 auditor like Thoropass?

Thoropass brings experienced SOC 1 auditors, a structured audit process, and an audit lifecycle platform together in one connected experience. That helps your team reduce manual coordination, improve visibility, respond to evidence requests more efficiently, and move toward the final SOC 1 report with greater confidence.