Eyebrow Text
Support for the requirements your industry demands
Organizations often need to manage more than one cybersecurity framework. Customer expectations, regulations, contracts, geographic expansion, and the type of data you handle can all introduce new audit and assessment requirements over time.
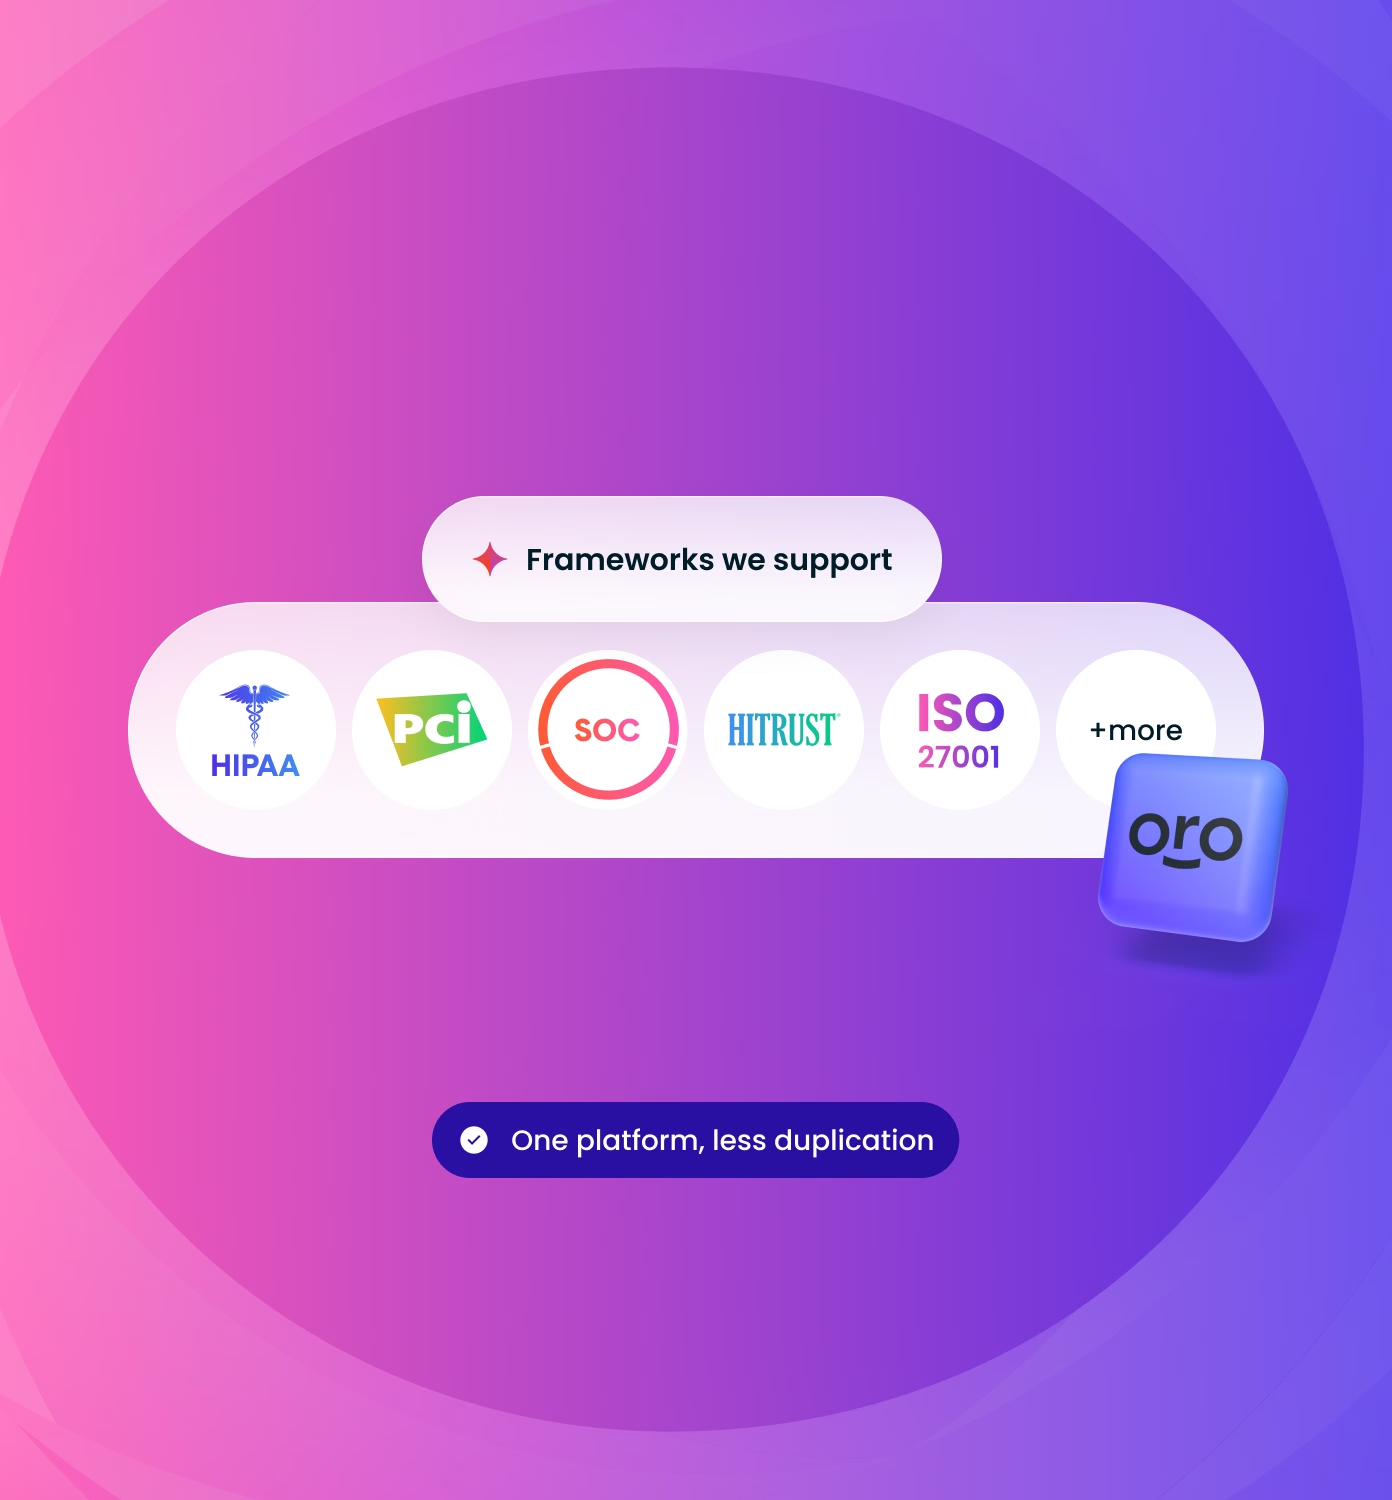
Thoropass supports organizations across frameworks including SOC 1, SOC 2, ISO 27001, PCI DSS, HITRUST, HIPAA, CMMC, and others.
Our Audit Lifecycle Platform helps bring evidence, communication, and audit activity together, making it easier to manage individual engagements and reduce unnecessary duplication when requirements overlap.